Dinarian888
News • Business • Investing & Finance
🌐 ISO 20022: to March and beyond – Deutsche Bank 🌐
January 08, 2023
post photo preview

SWIFT plans to introduce a central Transaction Manager (TM) platform, which will be mandatory for all SWIFT users. This article provides an update on ISO 20022 payments standard migration so far...

The upcoming implementation of ISO 20022 in the high value payments (HVP) space is set to unlock a host of benefits for the cross-border payments industry – from improved compliance processes to the creation of innovative products and services. Deutsche Bank’s Joey Han explores how preparations are ramping up – and what we should expect as we transition into the ISO 20022 era

The origin of ISO 20022 dates back to 2004, when it was first recognised by the International Organisation for Standardisation (ISO) as the global payment standard of the future. Eighteen years later, this future has nearly arrived. Once Society for Worldwide Interbank Financial Telecommunications (SWIFT) and major payment market infrastructures (including T2, Fedwire/CHIPS and CHAPS) have migrated to the new standard over the next couple of years, ISO 20022 will apply to the entire spectrum of payments, including domestic, automated clearing house (ACH), real-time and high value cross-border payments.

The new standard is comprehensive in scope, flexible in nature and will act as a harmonised, global standard. This comes at a critical time for the industry, with calls for seamless and faster payments growing louder – and it is hoped that these attributes can provide the foundation for uplifted customer experience, streamlined compliance procedures, and a host of new, innovative services.

The decision to migrate HVP to ISO 20022 gave rise to a multi-year, industry-wide set of preparations – involving all key actors, from financial institutions and corporates, to clearing infrastructures and SWIFT.

Over the past few years, however, the proposed migration strateĀ­gies have, for a variety of reasons, been somewhat of a moving target. Most recently, the European Central Bank (ECB) announced what is anticipated to be final change to its strategy, with the go-live date movĀ­ing from November 2022 to March 2023 to give participants additional time to complete their testing in a stable environment. In order to align with the ECB’s revised strategy – and to ensure the implementation is as straightforward as possible – both European Banking Authority (EBA) Clearing and SWIFT announced that they would also sync up their reĀ­spective migrations. The Bank of England is scheduled to migrate in April 2023 (though a deadline extension is also being considered), followed by The Clearing House and The Federal Reserve Banks in November 2023 and March 2025 respectively.

The differences in migration timelines and scope, as well as the fact that some banks will migrate immediately, while others will wait, is introducing a host of challenges – and ultimately delaying the benefits the new, data-rich payment standard can bring. So, how are these challenges being addressed, and what are the main considerations going forward?

Full steam ahead in APAC

The migration of domestic, HVP systems in Asia Pacific (APAC) are alĀ­ready well underway. In summer 2022, several ISO 20022 migrations took place across APAC. Paving the way for the rest of the world, Thailand’s RTGS system – known as Bank of Thailand Automated High-value Transfer Network (BAHTNET) – became one of the first payment infrastructures to introduce ISO 20022 this year, along with the Malaysian RTGS (RENTAS) and the Singaporean RTGS (MEPS+). Additionally, Australia will be going live in March 2023, with a co-existence period lasting until November 2024. New Zealand will also go live at the same time.

What can we learn from the early adoption of ISO 20022? Not all migrations are created equal. When moving to ISO 20022, banks operating in multiple markets have to navigate different geographical and regulatory conditions, as well as different technical approaches. Both a phased ā€œlike-for-likeā€ approach and a ā€œbig-bangā€ approach will also impact the migration project, operations and end customer in different ways.

Also, while the rules for how to use ISO 20022 messages are based on the market practices outlined by High Value Payments Systems Plus (HVPS+) and are in line with Cross-Border Payments and Reporting Plus (CBPR+), they are still not the same in every market. Close attention is needed to spot and prepare for these subtle differences – or risk a higher volume of rejects and further issues in payments processing.

ā€œThe ISO 20022 migration is much more than just a new messaging format, it is the start of an entirely new era for paymentsā€
Joey Han, Clearing Solutions Specialist, APAC, Institutional Cash Management at Deutsche Bank

Transaction management

Though several communities are already using ISO 20022, with the upcoming changes covering correspondent banking, the significance of the move to the new standard is much more far reaching. CorĀ­respondent banking largely relates to cross-border payments, but it also includes domestic payments between correspondents – or indirect participants – and their direct participants in the domestic HVP market infrastructures.

As part of its migration, SWIFT plans to introduce a central Transaction Manager (TM) platform, which will be mandatory for all SWIFT users. The TM will orchestrate transactions end-to-end, replacing the point-to-point messaging that is currently in use. The first interbank message in the payment chain will trigger the creation the Transaction Copy, which will then be updated with each subsequent message in line with strict data integrity rules. The improvements this will bring to end-to-end transaction integrity is one of the major drivers for the introduction of the platform. The technical deployment of the TM took place in November 2022, with no payment traffic expected until May 2023.

It will also play a key role in helping financial institutions navigate SWIFT’s co-existence phase (March 2023 to November 2025) – the period in which MT and ISO 20022 messages will remain interoperable – by removing the ā€œweakest linkā€ problem and mitigating the risk of data truncation. The TM will achieve this by maintaining a complete copy of the transaction data and reinstating any data that the intermediary agent could not include in the message type (MT) message. In line with the co-existence period – and the challenges it brings – many banks, such as Deutsche Bank, have promised to maintain their MT receiving capabilities throughout the entire co-existence period.Ā 

A while longer to wait

Though the TM will be a great asset to the industry, it will not be the silver bullet from day one. Before the full benefits of the TM can be unlocked, there will be a short period where it will not process any bank traffic and the processing rules will not be applied. This means that when the CBPR+ messages go-live in March 2023, and the first financial institutions begin to process data-rich ISO 20022 payments, the TM rules will not be apĀ­plied to these transactions.

With TM functionality not expected to be offered until May 2023, end-to-end preservation of rich data will not be guaranteed on any mesĀ­sages until then. Because of this, many financial institutions – including Deutsche Bank – are recommending that market participants avoid using the enriched data during the first few months of the migration phase to help reduce and mitigate any possibility of data truncation. This is in line with recommendations from the Payments Market Practice Group (PMPG).

From May 2023, the TM is scheduled to go through a three-stage, build-up approach to ensure platform stability and mitigate concentraĀ­tion risk. Over the course of the build-up period, SWIFT will be closely monitoring the payment channels and watching for high levels of traffic. If, at any particular time, an extraordinarily high volume of messages was detected, SWIFT would be able to react and help reduce the number of payments being routed through the TM by introducing additional routing criteria. Under current plans, SWIFT aims to achieve this by broadening or shortening the unique end-to-end transaction reference (UETR) range, as required. For instance, if a UETR range is limited to 1A-10, this means that only transactions with a UETR that includes the last two characters from this range will be routed via the TM.

Translation and truncation

SWIFT’s in-flow translation will act as a central translation engine to supĀ­port banks already using ISO 20022, as well as those that continue to use MT messages. ISO 20022 messages will be translated to MT and delivered as multi-format (ISO 20022 with embedded translated MT) messages. By translating ISO 20022 messages to the MT equivalent and delivering both formats to the receiver, the tool will play a critical role in supporting the co-existence phase, as well as compliance processes. A non-ISO 20022 enabled institution, for example, will use the ISO 20022 format to perform the necessary compliance due diligence, and use the MT format for processing.

But that is not to say there won’t still be issues with truncation. If a non- ISO 20022 enabled institution is acting as an intermediary in a transaction, it will not be able to send on the rich ISO 2022 data it receives – and will instead send on a truncated MT message.

There are two main types of truncations: those that are indicated by a ā€œ+ā€ in the body of the truncated messages (for ISO elements with direct MT equivalents), and those that aren’t (for ISO elements without direct MT equivalents). In the latter case, the elements unique to ISO will be mapped into the non-equivalent elements in fields 70 and 72. If the available space in these fields were filled, the elements of a lower translation priority would be dropped from the message.

The in-flow translation will, therefore, be particularly important during the first few months of the migration. With the TM not fully operational by until May 2023, the in-flow translation will provide a much-needed additional layer of protection. The translation report – that comes with each translated message – will identify instances of truncation, as well as provide detailed information on the translated MT. Where truncation is identified, CBPR+ has provided a standard, global template to be used for additional data requests.

Carry on testing

With the migration now in sight, what is left to do? Many of our clients have been reaching out to us asking about the possibilities of testing. In this respect, we have been as accommodating as possible regarding bilateral tests. And while it is clearly not feasible to test with every client, we have also taken steps to facilitate self-service activities.

For example, Deutsche Bank recently launched the DB Institutional Cash Management (ICM) Portal on SWIFT MyStandards. The portal aims to provide ICM usage guidelines (UGs) for pacs.008, pacs.009 and pacs.009COV, which are based on CBPR+ and enriched with Deutsche Bank annotations. These can be used as the basis for any testing activity on MyStandards.

As the deadline approaches, it is worth remembering the reason these efforts are being made. The ISO 20022 migration is much more than just a new messaging format, it is the start of an entirely new era for payments. It is a huge opportunity to fundamentally reassess and greatly improve existing business models and solutions. In doing so, it will help the payments community meet the changing needs of their clients – both now and in the future.

Link

community logo
Join the Dinarian888 Community
To read more articles like this, sign up and join my community today
0
What else you may like…
Videos
Podcasts
Posts
Articles
šŸŽ¬ The investment opportunity in Bittensor šŸŽ¬

@Briandixon06, CEO of Off The Chain Capital, and @GrantCardone discuss the investment opportunity in Bittensor.

$TAO 🌐 WYKYK šŸ˜‰

00:02:06
The Genie Is Out Of The Bottle šŸ‘€

JUST IN: šŸ‡ŗšŸ‡ø Former CFTC Chairman Chris Giancarlo says "the genie is out of the bottle" on crypto, and it’s going to consume the entire financial system šŸ‘€

"Wall Street itself is now adopting digital network technology as its very architecture." šŸš€

00:00:31
āš ļøā€¼ļøBANK CEO CONFIRMS THE FEDERAL RESERVE DELAYED HIS BANK FROM FLIPPING THE SWITCH TO CRYPTOā€¼ļøāš ļø

ā€¼ļøBANK CEO CONFIRMS THE FEDERAL RESERVE DELAYED HIS BANK FROM FLIPPING THE SWITCH TO CRYPTOā€¼ļø

Mike Ring, CEO of Old Glory Bank, explains on the record why his bank's crypto platform has not launched.šŸ’Æ

"So why have we not FLIPPED THE SWITCH and made this available?"šŸ™‡ā€ā™‚ļø

Old Glory Bank built NextGen Banking. One bank account with crypto built in.

Customers link their digital assets inside the bank and move between dollars and the blockchain.🌐

The launch was ready. A deal was in place for July 2026 with more than enough capital behind it.

The Federal Reserve cancelled it at the last minute.šŸ”»

"The Fed hates crypto. They do not want a bank like Old Glory Bank to be able to provide you, Main Street, an easy way to get on and off the blockchain."ā˜ļø

However, the bank is prepared with a plan B.šŸ”’

A new deal is in place and this one does NOT need the Federal Reserve.šŸ˜‰

"We're doing a deal that does not require Federal Reserve approval. They are not going to stop us. They cannot ...

00:03:04
🚨 Chutes is being framed as a Hyperliquid-style breakout for decentralized AI inference, with live revenue, verified GPU infrastructure, and a direct challenge to centralized cloud AI 🚨

Chutes is gaining attention as a decentralized AI inference platform that claims to combine real usage, cryptographic verification, confidential computing, and open-source infrastructure into a working production system. The thesis is simple: instead of trusting Big Tech clouds with AI workloads, users get a distributed compute layer built around verification and privacy.

šŸ”‘ Key points

šŸ”¹ Chutes is live in production and reportedly scaled to more than 1,170 active GPU nodes, including large numbers of Nvidia H200s and Blackwell-class hardware.

šŸ”¹ The platform says it has processed nearly 38 trillion tokens since launch across 53 deployed applications and more than 700,000 registered users.

šŸ”¹ The team reportedly cut unprofitable usage programs, reduced total token volume, and still improved revenue efficiency, with revenue per GPU rising sharply after removing subsidized traffic.

šŸ”¹ Chutes is using post-quantum cryptography, trusted execution environments, and Nvidia confidential ...

🚨 Chutes is being framed as a Hyperliquid-style breakout for decentralized AI inference, with live revenue, verified GPU infrastructure, and a direct challenge to centralized cloud AI 🚨
🚨 JPMorgan’s criticism of the CLARITY Act is fueling a fresh power struggle over who gets to write America’s crypto rules 🚨

A new clash is emerging between legacy finance and crypto legislation after JPMorgan CEO Jamie Dimon reportedly warned that the CLARITY Act could let crypto firms offer bank-like products without bank-level oversight. The dispute is quickly turning into a larger fight over regulation, competitiveness, and who controls the future architecture of digital finance in the United States.

šŸ”‘ Key points

šŸ”¹ Jamie Dimon reportedly called the CLARITY Act a threat to the financial system, arguing it could allow crypto firms to offer yield-like products while avoiding the capital, reserve, and oversight burdens traditional banks face.

šŸ”¹ Senator Cynthia Lummis pushed back publicly, framing the issue as a global strategic race and warning that if the U.S. does not set digital asset standards, other powers will.

šŸ”¹ The core tension is whether the bill creates legitimate regulatory clarity or simply opens the door to regulatory arbitrage for crypto platforms operating outside the traditional banking...

🚨 JPMorgan’s criticism of the CLARITY Act is fueling a fresh power struggle over who gets to write America’s crypto rules 🚨
šŸ‘‰ Coinbase just launched an AI agent for Crypto Trading

Custom AI assistants that print money in your sleep? šŸ”œ

The future of Crypto x AI is about to go crazy.

šŸ‘‰ Here’s what you need to know:

šŸ’  'Based Agent' enables creation of custom AI agents
šŸ’  Users set up personalized agents in < 3 minutes
šŸ’  Equipped w/ crypto wallet and on-chain functions
šŸ’  Capable of completing trades, swaps, and staking
šŸ’  Integrates with Coinbase’s SDK, OpenAI, & Replit

šŸ‘‰ What this means for the future of Crypto:

1. Open Access: Democratized access to advanced trading
2. Automated Txns: Complex trades + streamlined on-chain activity
3. AI Dominance: Est ~80% of crypto šŸ‘‰txns done by AI agents by 2025

🚨 I personally wouldn't bet against Brian Armstrong and Jesse Pollak.

šŸ‘‰ Coinbase just launched an AI agent for Crypto Trading
šŸ“š Time For AI Classes šŸ“–

Anthropic CEO Dario Amodei was asked what a kid finishing high school should do now.

His answer:

"AI can do entry-level law work. It can do entry-level finance. It can do entry-level consulting

We can't deny that it will also eliminate jobs, and probably a large number of them"

In a few minutes he names which jobs go first and the one skill that keeps you in the game

His own prediction: 50 percent of entry-level white-collar jobs disrupted in the next 1 to 5 years

Prompts → Agents → AI Coworkers → Entry-Level Work Done By AI

Farming to factories took generations. This time AI hits every step of a career at once

His advice fits in one line: "Of course, learn to use AI"

The people who start this year won't be competing with AI, they'll be the ones running it

Everything below is free. Start today:

Anthropic - Prompt Engineering Interactive Tutorial: the fastest way to learn to direct a model
https://github.com/anthropics/prompt-eng-interactive-tutorial

Anthropic Courses: from your first prompt to running agents
...

post photo preview
Its More Like AI Is The Biggest Risk To The Deep States Secrets šŸ˜‰

šŸ¤– AI tops the Fed survey’s financial-system risk concerns

A Federal Reserve survey found that AI-related risks have become the most frequently cited concern among respondents. The worries span a potential market correction, cybersecurity threats, and complex financing tied to the AI boom.

šŸ”‘ Key points

šŸ”¹ AI concerns climbed sharply: 87% of surveyed contacts cited AI as a salient risk, up from 50% in the spring survey.

šŸ”¹ Valuations could face pressure: Respondents warned that high AI-related stock valuations could fall if company earnings disappoint.

šŸ”¹ Cybersecurity threats are growing: Concerns include attacks by sophisticated state actors and potential damage caused by frontier AI models.

šŸ”¹ Financing structures add exposure: Survey participants also flagged risks from complex forms of AI-related financing.

šŸ”¹ Survey scope matters: The findings reflect views from 23 market contacts surveyed in September and October—not a prediction that a crisis will occur.

šŸ”Ž Why it matters...

🧠 Can TAO, alpha, and Gamma turn Bittensor into an AI economy?

Bittensor’s tokens may do more than attract capital: together, they could support a marketplace where businesses pay for subnet services. But real adoption depends on customers returning and paying enough to sustain those services.

šŸ”‘ Key points

šŸ”¹ TAO provides shared capital: Bittensor’s base token supports staking and helps capital move across the network.

šŸ”¹ Alpha tokens distinguish subnets: Each subnet has its own alpha token, and activity in alpha markets helps shape how network rewards are distributed. Holding alpha does not grant a legal claim on a subnet operator’s profits.

šŸ”¹ Gamma credits pay for services: Burning a subnet’s alpha creates a non-transferable, dollar-denominated credit redeemable for that subnet’s services.

šŸ”¹ Familiar pricing may help businesses: Dollar-denominated credits could make costs easier to compare with existing cloud bills, while providers handle token conversion behind the scenes.

šŸ”¹...

post photo preview
šŸŽÆWhat’s In Your Vault? — 2026 EditionšŸŽÆ

Sixteen years ago, I posed a question that appeared to be about money but was never really about money at all. What's In Your Wallet? was written at a moment when the world remained intoxicated by the illusion that a representation of value and value itself were interchangeable. The distinction seemed trivial because the machinery of modern finance operated smoothly enough to conceal it. A bank balance purchased goods. A brokerage statement could be exchanged for assets. A warehouse receipt represented commodities. A title represented property. A promise represented delivery. The system functioned, and because it functioned, few bothered to examine the assumptions upon which it rested.

Yet beneath the smooth functioning of the machine lurked a subtle substitution. Somewhere along the way we ceased valuing the thing and began valuing the description of the thing. We stopped demanding possession and settled for evidence of possession. We became comfortable owning records instead of realities, claims instead of assets, promises instead of substance. The map became more important than the territory because most people never wandered far enough from the roads to discover that the two were not the same.

Reading those observations in 2026 feels less like revisiting an old essay and more like observing a fault line that has slowly widened beneath the surface of the global financial order. What has changed is not the distinction itself. What has changed is that the institutions most responsible for maintaining the abstraction appear increasingly unwilling to trust it.

Around the world, central banks have begun bringing gold home. Not merely purchasing gold, though that is certainly occurring, but repatriating it. Bullion that once rested comfortably in the vaults of London and New York is being moved into domestic custody. Public explanations invoke geopolitical uncertainty, sanctions exposure, strategic resilience, and sovereign security. None of those explanations are incorrect. They are simply incomplete. They describe the circumstances without illuminating the realization that appears to be driving the behavior.

A gold bar in your vault is not the same thing as a claim upon a gold bar in someone else's vault. Since the Templars in Jerusalem communicating with the courts of Europe, promises are not the thing that's promised. They never were.

For decades that distinction could be ignored because confidence in the system remained sufficiently high that possession appeared unnecessary. The custodians were trusted. The networks functioned. The legal frameworks appeared durable. The infrastructure seemed permanent. Under those conditions, claims and assets could masquerade as equivalents because the distance between them was rarely tested. Yet every system eventually encounters moments when assumptions become visible. The freezing of sovereign reserves reveals that ownership and access are not identical. Financial crises reveal that liquidity and solvency are not identical. Infrastructure failures reveal that existence and availability are not identical. Again and again reality intrudes upon abstraction and reminds us that the world beneath the ledger still matters.

This is why the movement of gold deserves more attention than the declarations of economists, politicians, central bankers, or global forums. The repatriation of gold is not fundamentally a commodity story, an inflation story, or even a monetary story. It is a custody story. It is a sovereignty story. It is an acknowledgment that possession remains the final court of appeal whenever confidence begins to wobble.

The irony is difficult to miss. At precisely the moment civilization celebrates digital currencies, tokenized assets, algorithmic settlement systems, cloud-based records, and increasingly abstract forms of ownership, many of the institutions responsible for preserving national wealth appear to be moving in the opposite direction. Public narratives race toward virtuality while institutional behavior quietly migrates toward physical custody. The speeches point toward digitization while the bullion trucks point toward reality.

Perhaps nowhere does this contradiction become more visible than when contemplating the fragility of the infrastructure upon which modern finance rests. We speak confidently of balances, portfolios, reserves, pensions, derivatives, and increasingly digital assets as though they possess an existence independent of the systems that record them. Yet the entire architecture rests upon a remarkably delicate foundation of electricity, communications, computation, synchronization, and trust. We have become so accustomed to continuity that we mistake continuity for permanence.

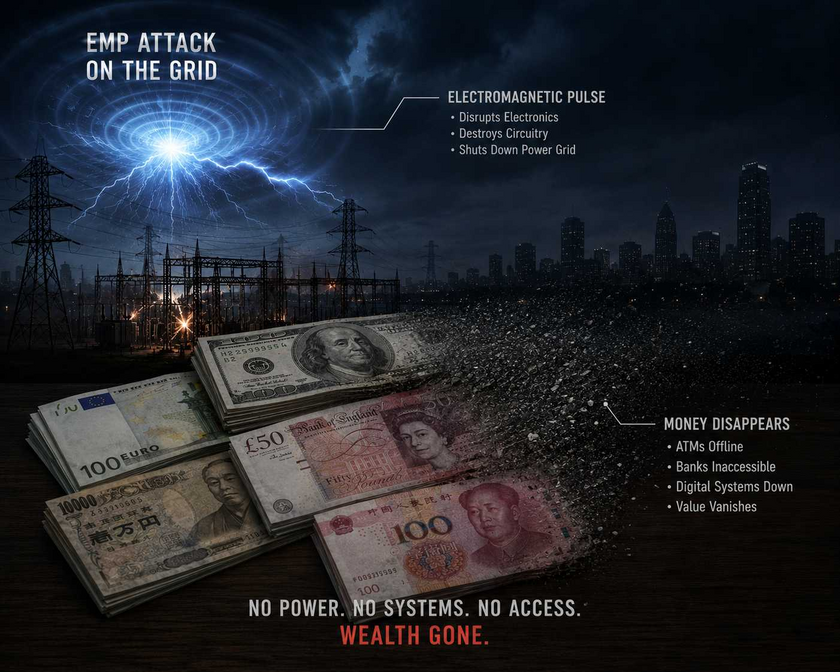
Consider not catastrophe but interruption. Consider a Carrington-scale solar event, a successful cyberattack, a cascading grid failure, or an electromagnetic pulse. The specific mechanism matters less than the principle. The lights go out. The servers stop responding. The networks cease synchronizing. The endless choreography of verification pauses. Legal claims may survive. Contracts may survive. Accounting entries may survive. Yet the practical ability to verify, transfer, access, or exercise those claims becomes uncertain. The abstractions remain theoretically intact while becoming functionally irrelevant.

Gold occupies a peculiar place within this thought experiment because it exists outside the thought experiment. It requires no password, no network connection, no authentication server, no intermediary, and no continuous electrical infrastructure to affirm its existence. The ledger may disappear. The gold remains. Whether one views gold as a monetary asset, a strategic reserve, or simply a historical curiosity, its persistence reveals something deeper about the nature of value itself. Assets that derive their existence from the systems that record them are fundamentally different from assets that exist independently of those systems.

What fascinates me, however, is not the rhetoric surrounding the so-called Great Reset, because the phrase itself has become one of the most effective distractions of the modern era. During the COVID years, populations were conditioned into increasingly reflexive forms of polarization in which every issue was immediately translated into opposing camps, every observation became a declaration of allegiance, and every question became a test of ideological loyalty. One side treated the Great Reset as evidence of a coordinated conspiracy while the other dismissed it as evidence of irrational paranoia. Both reactions produced the same outcome. Attention became fixed upon the slogan while remaining safely distant from the structure beneath it.

History has never required a committee to produce a reset. Resets emerge whenever claims become sufficiently detached from assets, whenever promises become sufficiently detached from productive capacity, whenever leverage becomes sufficiently detached from resilience, and whenever abstractions become sufficiently detached from reality. Long before a reset acquires a name, it exists as a tension embedded within the architecture itself.

This is why the most revealing actions in history are rarely the ones announced from podiums. They are the quiet movements that occur beneath the rhetoric. While populations argue over narratives, central banks move bullion. While commentators debate ideology, nations secure custody. While attention remains fixed upon political theater, the custodians of monetary power appear to be asking an older and more fundamental question concerning what survives when confidence falters, when access becomes uncertain, and when the systems responsible for recording ownership can no longer be assumed to function exactly as they did yesterday.

History repeatedly demonstrates that major transitions rarely emerge from the causes later assigned to them. Wars, sovereign defaults, financial crises, technological disruptions, infrastructure failures, and natural disasters frequently function as explanatory narratives that make visible contradictions that had already been accumulating for decades. The triggering event receives the blame because it is easier to understand than the architecture that rendered the event consequential. Yet the architecture is always where the real story resides. The event merely exposes what was already true.

Seen from this perspective, the most important question is not whether a particular organization intends to implement a Great Reset. The more important question concerns the conditions under which resets become inevitable. Whenever claims multiply faster than assets, whenever obligations expand faster than productive capacity, whenever financial abstractions drift sufficiently far from physical realities, tensions accumulate that eventually demand reconciliation. That reconciliation may arrive through inflation, restructuring, default, crisis, technological disruption, or events conveniently attributed to forces beyond human control, but the mechanism remains secondary to the principle. Reality eventually reasserts itself because reality is the only foundation upon which any abstraction can ultimately stand.

Viewed through that lens, the repatriation of gold appears less like a financial decision than an institutional acknowledgment that the distinction between claims and assets still matters. It represents a quiet recognition that resilience and possession acquire increasing importance precisely when complexity and uncertainty begin to rise. It suggests that beneath the public narratives, beneath the political theater, and beneath the endless distractions that dominate contemporary discourse, some of the world's most consequential actors may be asking the same question that inspired an essay sixteen years ago. What do you actually possess when the systems recording possession become uncertain?

The question is not fundamentally about gold. It is not fundamentally about vaults. It is not fundamentally about central banks. It is a question about the difference between a thing and a description of a thing, between ownership and access, between claims and assets, between abstractions and realities. It is the question that emerges whenever a civilization becomes sufficiently dependent upon representations that it forgets to examine the realities those representations are intended to describe.

Sixteen years ago I asked what was in your wallet. Watching nations quietly move bullion across oceans and into sovereign custody, the question feels sharper today than it did then. Not because the answer has changed, but because the institutions themselves appear increasingly unwilling to pretend that a claim and an asset are the same thing. The distinction sounded eccentric in 2010. It sounds increasingly obvious in 2026. The most interesting question is whether the rest of us will recognize the significance of that realization before history once again forces the issue on its own terms.

Source

šŸ™To support my work, Helping to keep the signal high and the noise low:

šŸ‘‰ Cashapp: $thedinarian

šŸ‘‰ Buy me a coffee: https://buymeacoffee.com/thedinarian

šŸ‘‰ PayPal: Scan the QR code below šŸ“² or Click Here:Ā 

šŸ‘‡ Crypto Donations šŸ‘‡

XRP: r9pid4yrQgs6XSFWhMZ8NkxW3gkydWNyQX
XLM: GDMJF2OCHN3NNNX4T4F6POPBTXK23GTNSNQWUMIVKESTHMQM7XDYAIZT
XDC: xdcc2C02203C4f91375889d7AfADB09E207Edf809A6

Read full Article
post photo preview
āš ļø90 DAYS WITHOUT THE GRIDāš ļø
Why Governments Are Preparing for Critical Systems to Fail

MIND BEND THEORY | DOCUMENTED INVESTIGATION

The United States is preparing major military installations to continue operating if civilian infrastructure goes down. Britain is telling households to prepare for days without essential services. India is warning that an attack on the financial system can weaken a nation. And the Bank of England is asking what happens when cyber defenses fail—not if they can prevent every attack.

Individually, each development has an explanation.

Put them beside one another, however, and a larger pattern becomes visible.

Over the span of only a few weeks, governments and financial authorities in the United States, United Kingdom and India have publicly discussed preparations for disruptions involving some of the systems modern society depends upon most:

Power.

Water.

Fuel.

Communications.

Banking.

Supply chains.

This does not establish that these governments are preparing for one secret event.

There is no public evidence of a coordinated countdown, predetermined blackout date or single intelligence warning connecting them.

But there is something here that can be documented.

Governments are increasingly planning around a question that sounds very different from traditional emergency preparedness:

What happens when the systems we normally assume will be available are no longer available?

And in the United States, that question has now reached the Pentagon.

DOCUMENT 01

UNITED STATES — FORTRESS AMERICA

On September 30, 2026, Defense Secretary Pete Hegseth established a program called FORTRESS America.

The acronym stands for:

Federal Operations for Resilience, Troop Resources, Energy, Supply and Survivability.

The program addresses a vulnerability that rarely receives much public attention:

The world's most powerful military still depends extensively on civilian infrastructure.

Electric grids.

Commercial supply chains.

Communications infrastructure.

Fuel.

Foreign sources of critical materials.

FORTRESS America is intended to reduce those dependencies.

The Pentagon's own public description says the initiative is designed to ensure that major U.S. military installations generate independent power so that bases remain operational even if the civilian grid is taken down by cyberattack or sabotage.

It goes beyond electricity.

The program includes five major areas:

Energy independence

Installation hardening and cyber resilience

Supply-chain and defense-industrial-base resilience

Strategic defense reserves

Space and spectrum resilience

The Pentagon also wants deeper reserves of critical supplies so military operations can continue when ordinary supply lines are disrupted.

The underlying idea is simple:

The military should be capable of functioning even when the infrastructure surrounding it cannot.

An October 7 implementation memorandum obtained by DefenseScoop shows that the Pentagon had already begun establishing the FORTRESS America Program Office and assigning officials to implement those objectives.

Then another piece of the story emerged.

DOCUMENT 02

THE 90-DAY REQUIREMENT

On October 25, Fox News published details from additional FORTRESS America documents its reporters reviewed.

According to that reporting, major continental U.S. military installations are being prepared to sustain essential operations for at least 90 days without outside support.

The essential systems reportedly include:

Power.

Water.

Fuel.

Communications.

Think about the distinction carefully.

The Pentagon isn't telling Americans that the United States will lose electricity for 90 days.

It isn't predicting a 90-day blackout.

Military contingency planning deliberately prepares for scenarios officials hope never occur.

But preparing installations for this possibility tells us something about the scenario being considered.

The Pentagon is building resilience around the possibility that a sufficiently serious conflict or attack could interfere with the civilian systems on which military installations normally depend.

The publicly released FORTRESS material specifically discusses:

Cyberattack.

Sabotage.

Grid disruption.

Foreign supply-chain disruption.

Attacks against installations.

And prolonged military contingencies.

That makes the 90-day requirement significant—but it must be described accurately.

Mind Bend Theory verification note:

The September 30 FORTRESS America program itself is documented publicly.

The October 7 implementation memorandum has been reported and described by DefenseScoop.

The 90-day requirement, however, currently comes from documents reviewed by Fox News, rather than a primary 90-day document independently published for the public.

That distinction matters.

We follow the documents as far as they take us—and no farther.

DOCUMENT 03

UNITED KINGDOM — BE READY FOR THREE DAYS

Now cross the Atlantic.

On October 22, the British government launched its new Be Ready campaign.

This time the audience wasn't the military.

It was ordinary households.

The UK government is asking households that are able to do so to prepare to remain self-sufficient for approximately three days during an emergency.

The government specifically discusses disruptions affecting:

Power.

Water.

Phones.

Internet access.

A Parliamentary Written Statement issued the same day explicitly states:

ā€œThe updated advice calls on households to be self-sufficient for three days in the case of an emergency.ā€

The government recommends maintaining three days of bottled water and non-perishable food.

Its expanded preparedness guidance includes:

Approximately three litres of drinking water per person per day

Three days of non-perishable food

Battery-powered or wind-up radio

Torch and spare batteries

Charged power bank

Essential medications

First-aid supplies

Blankets and warm clothing

Important telephone numbers written down

Basic hygiene supplies

Cash

Why cash?

Because during some disruptions, electronic payment systems and ATMs may not function normally.

That creates an important connection between infrastructure and finance.

Electricity isn't isolated from banking.

Communications aren't isolated from payments.

Modern infrastructure is interconnected.

And failure can move through those connections.

DOCUMENT 04

INDIA — ā€œWARS ARE NOT FOUGHT WITH WEAPONS ALONEā€

Three days later, on October 25, another statement appeared.

This one came from Indian Prime Minister Narendra Modi.

Modi was inaugurating the Reserve Bank of India's newly established Data Centre and Cybersecurity Training Institute in Bhubaneswar.

The facilities are designed to strengthen the technological foundations and cybersecurity resilience of India's financial system.

Four data centres will host mission-critical payment and settlement systems.

But Modi's explanation of why this matters went beyond ordinary cybersecurity.

His official statement says:

ā€œNowadays, wars are not fought with weapons alone; a nation can also be weakened by attacking its economy.ā€

He continued by saying India's growing economy requires its banking system to be protected against cyber looters and cyber terrorists.

That puts another critical system into the picture:

Money.

A modern economy depends on digital banking infrastructure almost as heavily as it depends on electricity and telecommunications.

Payment systems move commerce.

Banks hold liquidity.

Settlement systems move money between financial institutions.

Data centres keep those networks functioning.

Disrupt the financial infrastructure badly enough and the consequences don't remain inside banks.

They reach businesses.

Supply chains.

Payroll.

Purchasing.

Markets.

And households.

DOCUMENT 05

BANK OF ENGLAND — WHAT IF CYBER DEFENSE FAILS?

There is another document worth reading.

On June 30, Bank of England Deputy Governor Sarah Breeden delivered a speech titled:

ā€œAgents of Change.ā€

The subject was artificial intelligence and financial stability.

One section deserves particular attention.

Breeden warned that advanced AI systems are becoming increasingly capable of identifying and chaining together cyber vulnerabilities.

That changes the nature of cyber risk.

AI can help defenders.

But the same capabilities can potentially increase the speed and effectiveness of attackers.

The important change in thinking comes afterward.

Preventing attacks is no longer enough.

Financial institutions must also prepare to recover after a successful attack.

Breeden raised the possibility of simultaneous disruption across multiple financial firms.

She then asked whether critical financial institutions may eventually require completely separate failover capabilities—or even the ability to rebuild compromised core systems from ā€œbare metal.ā€

In October, Reuters reported that the Bank of England was pushing financial institutions further toward this type of recovery planning.

That represents a subtle but significant change in the question.

It isn't simply:

How do we stop the attack?

It's becoming:

What happens if we don't?

And:

How do we keep the system functioning afterward?

CONNECT THE DOCUMENTS

Now put the documents beside one another.

UNITED STATES

Military installations are being hardened so essential operations can continue when civilian infrastructure is disrupted.

UNITED KINGDOM

Households are being told to prepare for three days without services they normally assume will remain available.

INDIA

The prime minister publicly warns that modern conflict can weaken a country by attacking its economy and calls for stronger protection of banking infrastructure.

BANK OF ENGLAND

Financial authorities are examining recovery scenarios in which cyber defenses have already failed and multiple institutions could potentially be disrupted simultaneously.

These aren't identical programs.

They aren't even aimed at the same people.

And there is currently no public evidence demonstrating that they were coordinated.

But they share one important assumption:

CRITICAL SYSTEMS CAN FAIL.

And resilience therefore cannot begin after the failure occurs.

It has to exist beforehand.

THE SYSTEM BEHIND THE SYSTEM

This is where the story becomes bigger than individual announcements.

Modern infrastructure isn't a collection of isolated systems.

It's a network.

Consider what happens when electricity fails.

Without power, telecommunications eventually become difficult to maintain.

Without communications, electronic payments can be affected.

Fuel pumps require electricity.

Water systems depend on pumping and treatment infrastructure.

Businesses depend on payment processing.

Supply chains depend on communications, transportation and fuel.

Hospitals require electricity, communications, water, medicine and logistics simultaneously.

A serious disruption doesn't necessarily remain inside the system where it started.

It can propagate.

POWER → COMMUNICATIONS → BANKING → COMMERCE → SUPPLY CHAINS

And the dependency runs in multiple directions.

That interconnectedness is precisely why governments plan for resilience.

WHAT THIS DOES NOT PROVE

Mind Bend Theory exists to examine unusual patterns.

But a pattern isn't automatically proof of a conspiracy.

There is currently no public evidence showing that Washington, London and New Delhi are secretly preparing for the same scheduled event.

There is no verified date for a coming global blackout.

There is no public document establishing an imminent 90-day collapse of the American electrical grid.

And the Pentagon's 90-day military resilience requirement should not be interpreted as a prediction that Americans will lose electricity for 90 days.

That would go beyond the evidence.

What the evidence actually establishes is interesting enough.

Governments increasingly consider disruption of power, communications, supply chains and financial infrastructure plausible enough to justify concrete preparation.

The UK is preparing households.

The United States is hardening military infrastructure.

India is strengthening the technological backbone of its financial system.

The Bank of England is thinking about how banks recover after cyber defenses fail.

That isn't speculation.

It's in the documents.

THE QUESTION

Perhaps the most important change isn't what governments believe will happen.

It's what they're preparing to survive.

For decades, infrastructure security focused heavily on preventing failure.

The emerging model looks different:

Assume something eventually gets through.

Assume something eventually goes down.

Build the ability to continue operating anyway.

The Pentagon calls that resilience.

The UK calls it being ready.

Central banks call it operational resilience.

Different terminology.

Same fundamental question:

WHAT STILL WORKS WHEN THE SYSTEM DOESN'T?

DOCUMENT TRAIL

Read the Evidence Yourself

Mind Bend Theory strongly encourages readers to examine the original material rather than relying solely on our interpretation.

šŸ‡ŗšŸ‡ø DOCUMENT 01 — FORTRESS America Establishment

September 30, 2026

Defense Secretary Pete Hegseth's memorandum establishes FORTRESS America as a Department of Defense resilience program.

The publicly reported memorandum establishes the program around installation resilience, independent energy, strategic reserves, supply chains and related national-defense infrastructure.

Source type: Pentagon memorandum / official announcement.

šŸ‡ŗšŸ‡ø DOCUMENT 02 — FORTRESS America Implementation Memorandum

October 7, 2026

DefenseScoop obtained the memorandum from Under Secretary for Acquisition and Sustainment Michael Duffey directing officials to begin operationalizing the FORTRESS America Program Office.

It identifies five foundational pillars, including energy independence, installation hardening and cyber resilience, strategic reserves and supply-chain resilience.

Source type: Pentagon memorandum obtained by DefenseScoop.

šŸ‡ŗšŸ‡ø DOCUMENT 03 — 90-Day FORTRESS Requirement

October 25, 2026

Fox News reports that documents it reviewed require major continental U.S. installations to sustain essential operations for at least 90 days without outside support.

Source type: Journalistic reporting based on documents reviewed by reporters.

Important: This is not currently being presented by Mind Bend Theory as a publicly released primary 90-day Pentagon document.

šŸ‡¬šŸ‡§ DOCUMENT 04 — UK Cabinet Office Be Ready Announcement

October 22, 2026

The Cabinet Office announces the three-year Be Ready campaign and describes preparation for disruption affecting power, water, phones and internet.

Source type: Official UK government publication.

šŸ‡¬šŸ‡§ DOCUMENT 05 — Parliamentary Written Statement HCWS409

October 22, 2026

The UK Parliament records the government's explicit recommendation that households prepare to remain self-sufficient for three days.

Source type: Official Parliamentary record.

šŸ‡¬šŸ‡§ DOCUMENT 06 — Be Ready Household Emergency Checklist

The government's practical household guidance provides recommendations for water, food, radio, lighting, medication, power banks, emergency cash and other supplies.

Source type: Official UK government preparedness guidance.

šŸ‡®šŸ‡³ DOCUMENT 07 — Prime Minister of India / RBI Cybersecurity Facilities

October 25, 2026

Official statement documenting the opening of the Reserve Bank of India's Data Centre and Cybersecurity Training Institute and Modi's warning that countries can be weakened through attacks against their economies.

Source type: Official Government of India statement.

šŸ‡¬šŸ‡§ DOCUMENT 08 — ā€œAgents of Changeā€ — Sarah Breeden

June 30, 2026

The Bank of England deputy governor discusses rapidly advancing AI cyber capabilities, simultaneous disruption across financial institutions, separate failover infrastructure and potentially rebuilding compromised systems from bare metal.

Source type: Official Bank of England speech.

DOCUMENT 09 — Bank of England Cyber-Recovery Reporting

October 15, 2026

Reuters reports on the Bank of England's push for stronger recovery capabilities against AI-enabled cyberattacks, including bare-metal recovery.

Source type: Independent reporting.

MIND BEND THEORY

Follow the documents. Separate what they prove from what they don't.

Then ask why the preparation is happening now.

Documents attached to the investigation

FORTRESS America — Sept. 30 memorandum record
Pentagon FORTRESS America implementation memorandum — DefenseScoop
FORTRESS America 90-day documents — Fox News investigation
UK Cabinet Office — Be Ready announcement
UK Parliament — Written Statement HCWS409
India PM's Office — RBI Data Centre & Cybersecurity Training Institute
Bank of England — Sarah Breeden, ā€œAgents of Changeā€
Reuters — Bank of England cyber-recovery warning

Source

šŸ™To support my work, Helping to keep the signal high and the noise low:

šŸ‘‰ Cashapp: $thedinarian

šŸ‘‰ Buy me a coffee: https://buymeacoffee.com/thedinarian

šŸ‘‰ PayPal: Scan the QR code below šŸ“² or Click Here:Ā 

šŸ‘‡ Crypto Donations šŸ‘‡

XRP: r9pid4yrQgs6XSFWhMZ8NkxW3gkydWNyQX
XLM: GDMJF2OCHN3NNNX4T4F6POPBTXK23GTNSNQWUMIVKESTHMQM7XDYAIZT
XDC: xdcc2C02203C4f91375889d7AfADB09E207Edf809A6

Read full Article
September 13, 2026
post photo preview
Revolut Leak Shows the Cost of Constant ID Collection
Revolut’s mistake is the news, but the bigger problem is the growing number of companies being encouraged or required to keep copies of our most sensitive identity documents.

Online bank Revolut has revealed that it gave out sensitive personal and financial information of an undisclosed number of its customers in response to a fake government request.

The information that was handed over to an ā€œunauthorized third partyā€ reportedly includes names, dates of birth, occupations, addresses, phone numbers, account numbers, transaction histories (including Bitcoin), and even copies of government-issued IDs and onboarding verification selfies.

Revolut claims that derived biometric face data was not.

The company said that the data was handed over in response to an email that came from a real government agency’s domain, but was not actually sent or authorized by that agency.

The email passed several authentication checks (SPF, DKIM, and DMARC) that are designed to establish the authenticity of a message’s origin and integrity, but do not verify the legitimacy of the legal request itself.

Revolut said that it complied with the request ā€œunder the reasonable belief that it was an authentic government agency requestā€ – and only later found out that it was not.

Revolut said it later realized its mistake, blocked the email address, and reported the incident to the relevant authorities.

Revolut said that only a ā€œlimitedā€ number of its customers were affected by the data leak, and that the company’s systems were not hacked, nor was any money stolen.

The story broke on September 11 when Revolut customers started receiving an email notice about a data leak, and the news was picked up by media outlets the following day.

Revolut notice explaining customer identity and financial data was shared after an unauthorized government email request.

The reason this is a recurring problem is that companies are keeping highly sensitive information about their customers’ identities, and sometimes even financial transactions, for a long time, and this data is then available to be disclosed to third parties – either in response to valid legal requests, or, as in the case of Revolut, fake ones.

One reason for this is know your customer (KYC) and anti-money laundering (AML) rules. Revolut’s current UK customer privacy notice spells it out: the company generally keeps personal data of UK customers for no more than seven years after the relationship ends, and sometimes longer – for legal reasons.

This means that even if you close your account, your identity documents don’t disappear.

And while the incident with Revolut happened in the financial sector, it’s by no means the only one that requires customers to hand over sensitive identity information. Discord, a popular chat service, said in an October 9, 2025 security update that government ID photos of approximately 70,000 users may have been exposed after a third-party customer service provider got hacked.

This was not a financial service, nor the same type of attack. But the result was similar – because the underlying business process was the same: requiring and storing sensitive identity documents. In the case of Discord, these were used to review age-related appeals.

It’s hard to do anything about a copy of your old passport, or a photo of your face, or a record of your past transactions. These can be used to identify and profile you, and can be used to carry out targeted fraud. And this can happen even if the initial disclosure didn’t result in financial loss.

The more companies are forced to collect and store such information, and the more of it they have, the more opportunities there are for this data to be leaked, either by the company itself or a third party it works with. That's what makes governments' push for more ID checks just to access ordinary parts of life so reckless.

Source

šŸ™To support my work, Helping to keep the signal high and the noise low:

šŸ‘‰ Cashapp: $thedinarian

šŸ‘‰ Buy me a coffee: https://buymeacoffee.com/thedinarian

šŸ‘‰ PayPal: Scan the QR code below šŸ“² or Click Here:Ā 

šŸ‘‡ Crypto Donations šŸ‘‡

XRP: r9pid4yrQgs6XSFWhMZ8NkxW3gkydWNyQX
XLM: GDMJF2OCHN3NNNX4T4F6POPBTXK23GTNSNQWUMIVKESTHMQM7XDYAIZT
XDC: xdcc2C02203C4f91375889d7AfADB09E207Edf809A6

Read full Article
See More
Available on mobile and TV devices
google store google store app store app store
google store google store app tv store app tv store amazon store amazon store roku store roku store
Powered by Locals