Dinarian888
News • Business • Investing & Finance
Rilide: A New Malicious Browser Extension for Stealing Cryptocurrencies
April 14, 2023
post photo preview

(Dinarian Note: Whenever possible, ALWAYS go directly to the source versus clicking on an email link or google ad. Note: When searching on Google, the first 3 or 4 results are ads, do NOT use those. Also, ALWAYS double-triple check your pasted wallet address when withdrawing funds and ALWAYS use a VPN and Antivirus-Malware program, especially when you own crypto. Having cold storage is great, but when sending-recieving funds you are vunerable. Question everything, even if it seems legit.)

Trustwave SpiderLabs uncovered a new strain of malware that it dubbed Rilide, which targets Chromium-based browsers such as Google Chrome, Microsoft Edge, Brave, and Opera.

Rilide malware is disguised as a legitimate Google Drive extension and enables threat actors to carry out a broad spectrum of malicious activities, including monitoring browsing history, taking screenshots, and injecting malicious scripts to withdraw funds from various cryptocurrency exchanges.

Rilide is not the first malware SpiderLabs has observed using malicious browser extensions. Where this malware differs is it has the effective and rarely used ability to utilize forged dialogs to deceive users into revealing their two-factor authentication (2FA) and then withdraw cryptocurrencies in the background. During our investigation into Rilide’s origins, we uncovered similar browser extensions being advertised for sale. Additionally, we found that part of its source code was recently leaked on an underground forum due to a payment dispute.

Malicious Campaigns Leading to Rilide Stealer Extension

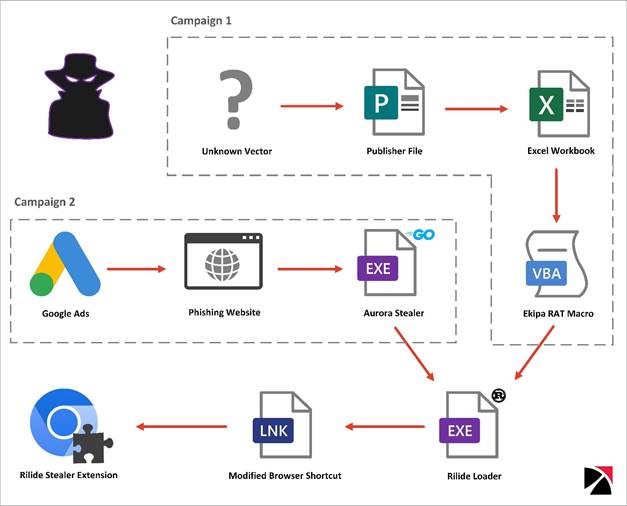
SpiderLabs uncovered two malicious campaigns leading to the installation of the Rilide extension.

Figure 1. Infection Chains Leading to the Execution of the Rilide Extension

Campaign 1: Ekipa RAT Installing Rilide Stealer

One of the Rilide samples identified by Trustwave SpiderLabs was distributed through a malicious Microsoft Publisher file. This file is part of Ekipa RAT, a Remote Access Trojan (RAT), designed for targeted attacks and often sold on underground forums.

We previously described Ekipa RAT in one of our blogs. It is important to note that Microsoft Publisher was not affected by Microsoft's decision to block macros from executing files downloaded from the Internet. As a result, when a user attempted to open a Publisher file, they would receive a warning but could still enable the execution of malicious content by clicking the ‘Enable Macros’ button. On 14 February 2023, Microsoft issued an update that resolved the Publisher security flaw. With the implementation of the ‘Mark of the Web’ feature on the .pub file, users are now left with only one option, ‘Disable Macros,’ which should have been the case all along.

Any association between the threat actors behind Ekipa RAT and those using the Rilide infostealer remains unclear. However, it is probable that Ekipa RAT was tested as a means of distribution for Rilide, before finally switching to Aurora stealer.

Figure 2. Publisher’s macro and Document_Open procedure executing remote Excel Workbook

Three tasks were configured on the C2 server:

  1. Download payload from hxxps://nch-software[.]info/1/2[.]exe to %temp% directory as.txt
  2. Change downloaded file’s extension to .exe
  3. Execute the payload.

File 2.exe is a Rust-based loader, responsible for installing the Rilide extension for Chromium-based browsers.

Campaign 2: Aurora Stealer Abusing Google Ads

Aurora is a Go-based stealer, which was initially spotted being advertised in April 2022 as a Malware-as-a-Service (MaaS) on Russian-speaking underground forums. The malware is designed to target data from multiple web browsers, cryptocurrency wallets, and local systems.

Recently, the threat actors behind Aurora have been observed abusing the Google Ads platform to spread the malware. According to a report published by Cyble, campaigns mimicking legitimate Team Viewer installers have been utilized to deploy Aurora. As reported by @1ZRR4H and @malwrhunterteam, Aurora was also spread via another campaign that imitated an NVIDIA Drivers installer. A downloaded sample was packed with Themida, a well-known commercial protector for executables. We used the UnpacMe service to unpack the sample.

Figure 3. Aurora campaign imitating the NVIDIA Drivers installer as shown in 1ZRR4H’s Twitter post

Restoring Function Names

The Aurora Stealer sample was stripped of debugging symbols, thus making the analysis harder. Since Go binaries are statically linked, which means that all the necessary libraries are included in the compiled binary, the number of potential functions to analyze is large. However, the original function names can be restored from the pclntab structure, as described in the CUJOAI Senior Threat Researcher Dorka Palotay’s post. Using the go_func.py script for Ghidra we were able to restore the functions names.

How an Aurora Module Downloaded Rilide Stealer

One of the eight grabbing modules, configured in the analyzed sample, contained a base64 encoded blob of data storing the URL for the Rilide Rust-based loader. The payload, hosted on Discord CDN, was saved to the %temp% directory with filename <10-alpahnumeric-characters>.exe and executed via start-process PowerShell cmdlet.

Figure 4. Part of Aurora Stealer routine downloading and executing Rilide loader

The Common Link Between Two Campaigns

The Rilide Rust-based loader samples analyzed as part of the Aurora campaign were packed with a VMProtect commercial packer. After unpacking the samples and analyzing strings contained in the binary, we found multiple references to Windows paths in the C:\Users\ilide\ directory. The same username was observed in the PDB Path of the Rilide sample obtained from the Ekipa RAT campaign.

Figure 5. The same username in a path found in Rilide Rust-based loaders samples from both campaigns.

Rilide Stealer Extension Targeting Chromium-Based Browsers

Rilide leverages a Rust loader used to install the extension if a Chromium-based browser is detected. Rilide mimics benign Google Drive Extensions and abuses several built-in chrome functionalities. The loader modifies LNK shortcut files opening targeted browsers, so that they are executed with parameter --load-extension pointing to the dropped malicious Rilide extension.

Figure 6. Rilide Stealer extension mimicking Google Drive and looking at its manifest revealing the configured permissions

Rilide’s background script attaches a listener to the tabs.onActivated and webRequest.onHeadersReceived events and removes the Content Security Policy (CSP) directive for all requests. This allows the extension to perform an XSS attack and load external resources that would otherwise be blocked by the CSP. The app script adds another listener to the DOMContentLoaded event and retrieves a list of targeted domains from the C2. If the current domain matches any of the listed targets, designated scripts are injected into the webpage.

Figure 7. Configuration list indicating targets such as email services and cryptocurrency exchanges.

Additionally, the background script carries out regular checks on the browsing history and exfiltrates URLs that are matched against the targeted domain list. Moreover, it is capable of capturing and exfiltrating screenshots of the currently active tabs on demand.

Figure 8. Rilide Stealer Execution Flow and Functionalities

Automatic Cryptocurrency Withdrawal

Rilide’s crypto exchange scripts support automatic withdrawal function. While the withdrawal request is made in the background, the user is presented with forged device authentication dialog in order to obtain 2FA. Email confirmations are also replaced on the fly if the user enters the mailbox using the same web browser. The withdrawal request email is replaced with a device authorization request tricking the user into providing the authorization code.

Figure 9. Withdrawal Requests replaced with Authorize New Device emails in Gmail mailbox

Figure 10. Content of the original and forged email. The verification code was extracted from the original message body.

We found no substantial variations in the code between the samples dropped by Ekipa RAT and used in the Aurora Stealer campaign. Both campaigns utilized a Rust dropper, and the functionalities of the browser plugins are nearly the same.

Figure 11. Code differences between Rilide Stealer plugin samples, both using the same C2 server

Rilide Stealer Origins

In the course of our research, we have encountered several stealer extensions for sale that advertised capabilities closely resembling those of the Rilide samples. However, we were unable to definitively link any of them to Rilide. One noteworthy finding was a botnet sale advertisement from an underground forum dated March 2022. Although the advertised functionalities matched those of Rilide, the botnet also included additional features such as a reverse proxy and ad clicker. Notably, the botnet's automatic withdrawal function supported the same exchanges observed in the Rilide samples.

Figure 12. Underground forum post advertising sale of botnet with Rilide-like capabilities

On February 27, 2023, a member of the same underground forum posted a link to the source code for the Rilide extension, reportedly due to an unresolved payment dispute. The leaked source closely resembles that used in the Aurora Stealer campaign but did not contain any of the injected scripts observed in the campaign sample.

Figure 13. Underground forum post, dated February 27, 2023, containing a link to part of the Rilide extension source code.

Notably there is one feature implemented that is missing in the later versions - swapping cryptocurrency wallet addresses in the clipboard. The list of addresses to be replaced is hard coded in the source code.

Figure 14. Clipboard hijacking routine in the analyzed sample from the forementioned forum post.

Pivoting on the Command-and-Control domain ashgrrwt[.]click hard coded in the sample, we identified additional Rilide loaders leading us to the GitHub user gulantin.

Figure 15. Github repository storing multiple Rilide loader and extension samples

Repositories created by this user contain loaders for the Rilide extension, but they are not Rust-based. The sample in the repository named ‘77’ is a .NET extension loader only for the Chrome browser, unlike the later Rust-based version that works for all Chromium-based browsers. Other loaders found in repositories 19 and 789 are based on Advanced Installer – a legitimate Windows Installer Packaging Tool for MSI installers.

Figure 16. Extension loading routine of the custom .NET loader from gulantin’s repository 77

The address contained in the domain variable that is supposed to store the C2 domain suggests that this version of a loader was still under development when submitted to GitHub.

Figure 17. Part of JavaScript configuration in the Rilide extension hosted on GitHub

Conclusions:

The Rilide stealer is a prime example of the increasing sophistication of malicious browser extensions and the dangers they pose. Disguised as a legitimate Google Drive extension, Rilide provides threat actors with the ability to carry out a wide range of malicious activities, including monitoring browsing history, capturing screenshots, and injecting malicious scripts to steal funds from cryptocurrency exchanges.

While the upcoming enforcement of manifest v3 may make it more challenging for threat actors to operate, it is unlikely to solve the issue entirely as most of the functionalities leveraged by Rilide will still be available.

Informational overload can dull our ability to interpret facts accurately and make us more vulnerable to phishing attempts. It is important to remain vigilant and skeptical when receiving unsolicited emails or messages, and to never assume that any content on the Internet is safe, even if it appears to be.

Ultimately, it is crucial to stay informed and educated about the latest cybersecurity threats and best practices to minimize the risk of falling victim to phishing attacks.

Indicators of Compromise:

Publisher File:

File name

Hash Type

Hash

Tes7777.pub

SHA256

0e31ff6406b03982581246b7dd60f3b96edcf0bd007b31766954df001fd68f69

SHA1

e049f56198c23d86e9083142bfe80042e21d4b8e

MD5

558104b26ccadec3d3eb2925113387a6


Aurora Stealer:

File name

Hash Type

Hash

PackageLauncher.exe

SHA256

e623984143e0dc6e35c79869ab1521c6714e588e8e648606496f8372ca0d8416

SHA1

b1c100d5a99ae34ccb3654c7b7f8573376a44fd9

MD5

c28a180de1f80c8c98d0904e64142bef

-

SHA256

ebd72806abd354f3162eec0991d127f993a5dde1a0c719b47087c9ee0edefeaf

SHA1

abaaa2644b1e84e8b39119988dd711572377c839

MD5

1baaeedd1a26edf4fa79ded370e3d19a


Rilide Loader:

File name

Hash Type

Hash

2.exe

SHA256

0f11aeecbde1f355d26c9d406dad80cb0ae8536aea31fdddaf915d4afd434f3f

SHA1

b4b918a5898463dad1c7d823e0b3f828bac15aad

MD5

0a4f321c903a7fbc59566918c12aca09

waBp.exe

SHA256

8342b134cddeaf34ce05bafa9e860dacf6cd01b85fd00147d90a350516c055e5

SHA1

25f3fb6d2dab206a5e9b2c0ef26ec6d6a56c5767

MD5

561797d7e5cf956e33735180d93be5b6


Rilide Extension:

File name

Hash Type

Hash

background.js

SHA256

4cc83be0fa496855d244050616ee2e86b044a9bc87bc5ca70b305986c1ba3bb8

SHA1

70167e7e5d71fba7d92796324b488c0fb9727712

MD5

766d020e902b6470d0510e5c6cfcd6e8

background.js

SHA256

55251c725e9f6f51b8db7a631b54dd85b1b59d644c3219e03ceffb0c49cd00a4

SHA1

a39d252e7927ae1adf518e6a3dd08f37e7ee7c26

MD5

d9cca3dd5bdaeb0466d52821b584602b

background.js

SHA256

1b01c3e554700e1282c7fdd2dcb54314516ee1f0c5eef3560cdbabc1ba776293

SHA1

ffebf78a9692293a23f9a477ea8a79f7f6ef5aa2

MD5

9e5f43b2dc1606e27fa0cfdfb4e363d2

app.js

SHA256

a28c623d120a76dcfeef9504eaeefabac9d33f292576ccf012fa458b8d7bc6ef

SHA1

a46586bfe22f4d84cd9174238740af275bf50c69

MD5

740606987f4d588c89d0a5b68648e31e

app.js

SHA256

8989f4244667626728c6c0083422ff714cb622c92c35a53f9cb1e9891f4528ff

SHA1

5012e783b2ee29cb40b04a10d1a40d0bfda683d9

MD5

1c54dd00bc7cc52b60ad4a46e2fb3a77

vpn.js

SHA256

170a13a7a8757336babe857804fa24b6cb20aaa9593b32546d7151f23095a510

SHA1

eafdc35b233600ef552b87e684faa3ab3396eae9

MD5

d54fa225b07298ec34be872cd4ebf4ae

manifest.json

SHA256

bb57a504e0b821552344cecb3da9ecdd0d61817264617a4917d6f5e64a1df7e5

SHA1

0cb1d9c2a3c8b776ef1e3ec1316fbf595ced7863

MD5

baee9ba0b94ea1e2b2e566fc8a615554

manifest.json

SHA256

d70e933e10e667ae7ef6e68a625c447be8aabe9b29affdad999c969bd8769003

SHA1

84db08e3dcbe40c7cbc998a77788f7303d4a2905

MD5

99dc4073f2fe91f48fd16bc65e7dcbc2

binance.js

SHA256

c8939f8d6237fcc17d486981a800b1e7e9974377de21d7e76677babe8ed536af

SHA1

f689396c73055e99a06e002c39e3a74d3d402607

MD5

2cc204564b68c5a98b1ff68d861b66c5

bitget.js

SHA256

2e310391d77022bcc708c354140319718777ca35efdfb76d6c80cb9de8c8091e

SHA1

05536aa80f8280ddc31be5c0ac3ca995f2190a0a

MD5

646b9404a29febe9f3741797b79e300c

blockchain.js

SHA256

4bbb0584eed0c082b5c43d3f259f37cf1a0b64eabb485e85090951a6566d98d4

SHA1

28ae2440c56350f65b607e4e99b67a2632db873b

MD5

253f4319673673d2bf5285558a6903df

bybit.js

SHA256

9dca66f52f31dca921fb238bd36bfc1b1a59d3e4af7b071da9bc4c6bf294e402

SHA1

61acdad59223a9eb0b392ccd085db1e49700d65

MD5

50e363409ba77b20fb6f0bce4eff7b1

coinbase.js

SHA256

4df0f18a7e05518bbe93758e751f1f462fef212cdc786c7217d50ddbda14efb5

SHA1

39f546a4ec94e63e603e3c2481fecab2b5e8a475

MD5

c1f40584e4ac391d97218ce137a63fb3

ftx.js

SHA256

ef20c929f5204b223b6e53dc406ea0bcd76d9e98c9ae4942037902883d4bb22a

SHA1

0ead1d32ce6b15c4a90373fce58d1554035cd40f

MD5

ebce63fdc8ef245f117f06ada3ba0f6d

huobi.js

SHA256

e1ad66cc0244fc075e0aabe0fd19502d4c9617829b90aa210e74be1d915275d2

SHA1

2449e4b27d778f6a4ffc00bb7b73926ac2c54e8a

MD5

4abe60d2c3506f4767e163d135f89f92

kraken.js

SHA256

a7f0fdfdfdf1ef65799fd2114bf5c1e133a8b7635b498b334553fbb64b218a05

SHA1

ec6de82efa93e59da148f4d696efcfca851e051e

MD5

b85c5659e946b5d7ad78410356288928

okx.js

SHA256

68278b40b59b1b0db2f814d2d864f0b9c2b4285f5795d22cabf60715f922989c

SHA1

415d790b54ca8e374f37fdbb00090110b823ba18

MD5

ff4e2df1a46d49862ab2a0af830a007e

gmail.js

SHA256

2f947644c7752ba014eae7971b247be60249a6088923c66ffe9886a7f5c5fe1c

SHA1

add0d61399c8c47f8ac73dc83cc83dfa31cddeca

MD5

c0e120778853f0a4865e006a07cd728a


Phishing Websites:

Malware

Domain

Aurora

nvidia-graphics[.]top


C2 Servers:

Malware

Domain

Ekipa RAT

nch-software[.]info

Aurora

45[.]15[.]156[.]210

Rilide

vceilinichego[.]ru

Rilide

ashgrrwt[.]click


Wallet Addresses:

Cryptocurrency

Address

BTC

bc1qkczacyp5jq29s5kaphth4asu8cv2y4u4gdgj7q

BTC

bc1qsjg8dqx6ga30h6szjd8dv2wg50ch50qrey4t7j

BTC

1KqequymujeNJuyB4gH7oJSFTB3En3Hf5n

ETH

0xDBc1330056E2F5e2FB11FB3C96dE2c44B313eA8d

LTC

LRYpzmnqBVozkbzJhTWndzYDPfjmNPyaLv

XRP

rUPTadzFN6LS662Z2d2AvNyqU1xwg2japJ

TRON

THiD8hFLiEyULVKLp3DSbBXQSbR3MQxm4X

DOGE

D5asYfjtbTtFmFkrEwqVgbJKYv9YT7Tgjh

Link

community logo
Join the Dinarian888 Community
To read more articles like this, sign up and join my community today
0
What else you may like…
Videos
Podcasts
Posts
Articles
Just A Few Use Cases For KOMMS SN27 On Bittensor 😉

Hint: 🔥 sale right now 😉

https://taostats.io/subnets/27/chart

00:01:13
🧠 Macrocosmos releases IOTA Decide 4B, its first public model 🧠

Macrocosmos has released IOTA Decide 4B, an open-weight model designed to return structured probabilities for choices such as support-ticket categories, urgency levels, and eligibility checks. Its weights are available under the Apache 2.0 license.

🔑 Key points

🔹 Outputs structured probabilities: Developers define possible answers, and the model scores each option in a single pass.

🔹 Built for software decisions: Potential uses include routing requests, flagging risky activity, checking eligibility, and deciding when a case needs human review.

🔹 Weights are openly licensed: Developers can download, adapt, and deploy the model under Apache 2.0.

🔹 Training used 879,000 examples: The model is based on Qwen3.5 4B and was trained on examples labeled by people, public datasets, and synthetic data.

🔹 Training spanned 16 GPUs: Macrocosmos says the distributed training used RTX A4000 GPUs connected across locations through its IOTA infrastructure.

🔹 Benchmark results are self-reported: ...

00:00:25
🖥️ TPN launches Gratis for private, on-device AI

TPN (SN65) has introduced Gratis, a free browser and desktop app for running AI models locally. Once a model is downloaded, conversations are processed on the user’s device and can continue offline—without an account or subscription, according to the project.

🔑 Key points

🔹 Models run on-device: Gratis uses the device’s own processing power, rather than sending each prompt to a cloud inference service.

🔹 Conversations stay local: The team says chats, attachments, images, and voice data remain on the user’s device.

🔹 Browser and desktop options: Gratis supports a browser version and desktop apps for macOS, Windows, and Linux.

🔹 Model recommendations included: The app checks available hardware and suggests models based on memory and processing capacity; users can also browse or load compatible Hugging Face models.

🔹 Offline use follows download: After the model is downloaded, users can chat without a remote inference service.

🔹 Performance depends on hardware: Available memory, ...

00:00:52
🚨 Chutes is being framed as a Hyperliquid-style breakout for decentralized AI inference, with live revenue, verified GPU infrastructure, and a direct challenge to centralized cloud AI 🚨

Chutes is gaining attention as a decentralized AI inference platform that claims to combine real usage, cryptographic verification, confidential computing, and open-source infrastructure into a working production system. The thesis is simple: instead of trusting Big Tech clouds with AI workloads, users get a distributed compute layer built around verification and privacy.

🔑 Key points

🔹 Chutes is live in production and reportedly scaled to more than 1,170 active GPU nodes, including large numbers of Nvidia H200s and Blackwell-class hardware.

🔹 The platform says it has processed nearly 38 trillion tokens since launch across 53 deployed applications and more than 700,000 registered users.

🔹 The team reportedly cut unprofitable usage programs, reduced total token volume, and still improved revenue efficiency, with revenue per GPU rising sharply after removing subsidized traffic.

🔹 Chutes is using post-quantum cryptography, trusted execution environments, and Nvidia confidential ...

🚨 Chutes is being framed as a Hyperliquid-style breakout for decentralized AI inference, with live revenue, verified GPU infrastructure, and a direct challenge to centralized cloud AI 🚨
🚨 JPMorgan’s criticism of the CLARITY Act is fueling a fresh power struggle over who gets to write America’s crypto rules 🚨

A new clash is emerging between legacy finance and crypto legislation after JPMorgan CEO Jamie Dimon reportedly warned that the CLARITY Act could let crypto firms offer bank-like products without bank-level oversight. The dispute is quickly turning into a larger fight over regulation, competitiveness, and who controls the future architecture of digital finance in the United States.

🔑 Key points

🔹 Jamie Dimon reportedly called the CLARITY Act a threat to the financial system, arguing it could allow crypto firms to offer yield-like products while avoiding the capital, reserve, and oversight burdens traditional banks face.

🔹 Senator Cynthia Lummis pushed back publicly, framing the issue as a global strategic race and warning that if the U.S. does not set digital asset standards, other powers will.

🔹 The core tension is whether the bill creates legitimate regulatory clarity or simply opens the door to regulatory arbitrage for crypto platforms operating outside the traditional banking...

🚨 JPMorgan’s criticism of the CLARITY Act is fueling a fresh power struggle over who gets to write America’s crypto rules 🚨
👉 Coinbase just launched an AI agent for Crypto Trading

Custom AI assistants that print money in your sleep? 🔜

The future of Crypto x AI is about to go crazy.

👉 Here’s what you need to know:

💠 'Based Agent' enables creation of custom AI agents
💠 Users set up personalized agents in < 3 minutes
💠 Equipped w/ crypto wallet and on-chain functions
💠 Capable of completing trades, swaps, and staking
💠 Integrates with Coinbase’s SDK, OpenAI, & Replit

👉 What this means for the future of Crypto:

1. Open Access: Democratized access to advanced trading
2. Automated Txns: Complex trades + streamlined on-chain activity
3. AI Dominance: Est ~80% of crypto 👉txns done by AI agents by 2025

🚨 I personally wouldn't bet against Brian Armstrong and Jesse Pollak.

👉 Coinbase just launched an AI agent for Crypto Trading

🛡️ Bittensor adds quantum-resistant wallet options in code

Bittensor’s wallet implementation now supports three post-quantum signature schemes, with optional automatic key rotation. The update is designed to protect TAO transfers, staking, and other wallet actions against future quantum-computing threats.

🔑 Key points

🔹 Three signature options: Users can choose ML-DSA-65, Falcon-512, or Falcon-1024.

🔹 Broad transaction support: The signatures work with coldkeys and hotkeys, covering transfers, staking, validator weights, and registration.

🔹 Optional key rotation: After a transaction, rotating wallets can switch to a fresh signing key while keeping the same address, balance, stake, and recovery phrase.

🔹 Rotation has a lock: Enabling automatic rotation requires a one-time 0.2 TAO lock; normal transaction fees still apply.

🔹 Existing wallets remain: Upgrading is optional, and current wallets continue to work.

🔎 Why it matters

🔹 Post-quantum security is moving from roadmap ...

🌎Schumann Resonance Today 11/8🌎

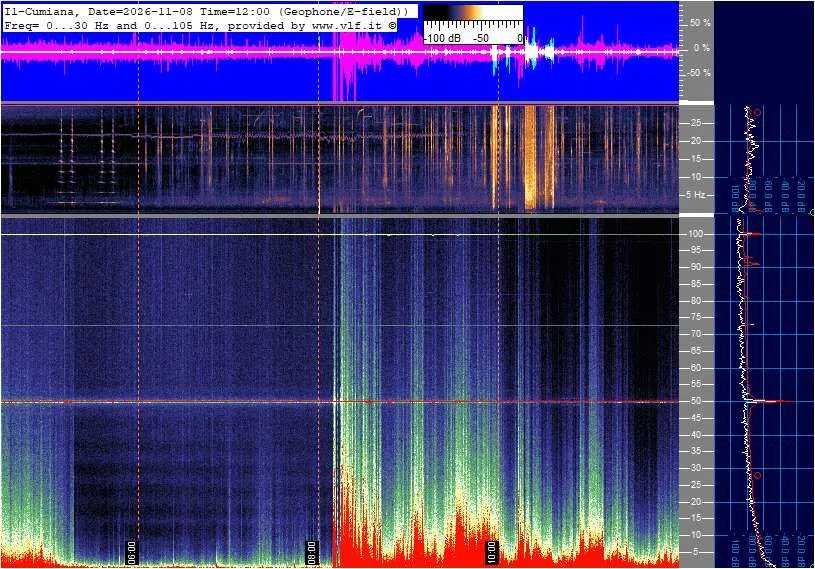
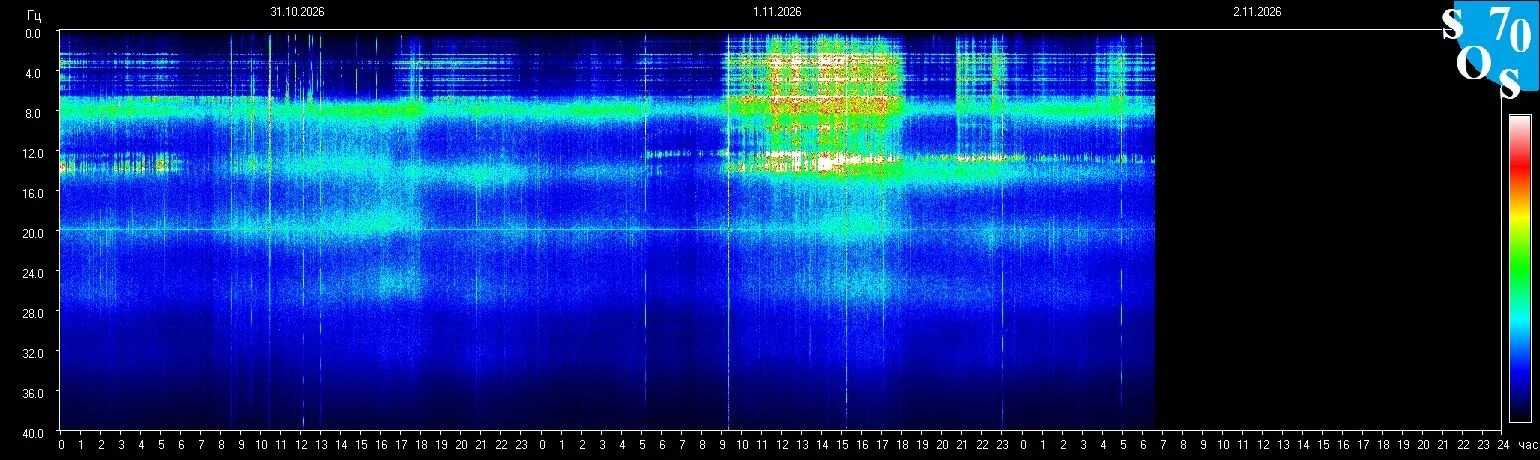
M-Class Flare, Fast Wind, Blind Spot Above: An M2.0 flare and solar wind topping 717 km/s are keeping the magnetosphere moderately stirred, while the Tomsk station remains in a six-day data blackout.

MOTHER EARTH IS SPIKING! WE ARE HEADING INTO A VERY CHARGED DAY! 🌏

Sunday, November 8, 2026 | Schumann Resonance & Solar Weather Update

Good morning, everyone! Mother Earth is showing some powerful activity this morning, and we could be heading into a very charged Sunday. The electric field chart is lighting up, we have a possible geomagnetic storm approaching, and the sun is becoming increasingly active. There are several things happening at once, and I think it’s a great opportunity to pay attention, learn a little science, and enjoy what Mother Earth is showing us.

🤔ARE YOU EXPERIENCING ANY OF THESE SYMPTOMS?

  • Ears ringing or increased tinnitus
  • Restless sleep or waking around 3–4 AM
  • Brain fog or difficulty concentrating
  • Head pressure or headaches
  • Bursts of energy followed by fatigue...

⚠️ Reports allege Chinese intelligence targeted Nvidia CEO Jensen Huang

A U.S. intelligence memo reportedly alleged that Alice Huang, a Singapore-based executive, was recruited to gather information on Jensen Huang and influence U.S. chip-export policy. These claims remain unproven; Nvidia says their interactions were routine business contacts and denies that sensitive information was shared.

🔑 Key points

🔹 Reported intelligence claims: Media reports describe a memo alleging Alice Huang was recruited by China’s Ministry of State Security.

🔹 Alleged policy objective: U.S. officials reportedly believed the effort sought information about Nvidia’s AI chips and support for sales to China.

🔹 Congressional scrutiny grows: Three House committee chairs have requested a closed-door briefing from Jensen Huang.

🔹 Nvidia rejects the allegations: The company says the interactions were ordinary customer-related contacts and no sensitive information was shared.

🔹 Claims remain unproven: The ...

post photo preview
🎯What’s In Your Vault? — 2026 Edition🎯

Sixteen years ago, I posed a question that appeared to be about money but was never really about money at all. What's In Your Wallet? was written at a moment when the world remained intoxicated by the illusion that a representation of value and value itself were interchangeable. The distinction seemed trivial because the machinery of modern finance operated smoothly enough to conceal it. A bank balance purchased goods. A brokerage statement could be exchanged for assets. A warehouse receipt represented commodities. A title represented property. A promise represented delivery. The system functioned, and because it functioned, few bothered to examine the assumptions upon which it rested.

Yet beneath the smooth functioning of the machine lurked a subtle substitution. Somewhere along the way we ceased valuing the thing and began valuing the description of the thing. We stopped demanding possession and settled for evidence of possession. We became comfortable owning records instead of realities, claims instead of assets, promises instead of substance. The map became more important than the territory because most people never wandered far enough from the roads to discover that the two were not the same.

Reading those observations in 2026 feels less like revisiting an old essay and more like observing a fault line that has slowly widened beneath the surface of the global financial order. What has changed is not the distinction itself. What has changed is that the institutions most responsible for maintaining the abstraction appear increasingly unwilling to trust it.

Around the world, central banks have begun bringing gold home. Not merely purchasing gold, though that is certainly occurring, but repatriating it. Bullion that once rested comfortably in the vaults of London and New York is being moved into domestic custody. Public explanations invoke geopolitical uncertainty, sanctions exposure, strategic resilience, and sovereign security. None of those explanations are incorrect. They are simply incomplete. They describe the circumstances without illuminating the realization that appears to be driving the behavior.

A gold bar in your vault is not the same thing as a claim upon a gold bar in someone else's vault. Since the Templars in Jerusalem communicating with the courts of Europe, promises are not the thing that's promised. They never were.

For decades that distinction could be ignored because confidence in the system remained sufficiently high that possession appeared unnecessary. The custodians were trusted. The networks functioned. The legal frameworks appeared durable. The infrastructure seemed permanent. Under those conditions, claims and assets could masquerade as equivalents because the distance between them was rarely tested. Yet every system eventually encounters moments when assumptions become visible. The freezing of sovereign reserves reveals that ownership and access are not identical. Financial crises reveal that liquidity and solvency are not identical. Infrastructure failures reveal that existence and availability are not identical. Again and again reality intrudes upon abstraction and reminds us that the world beneath the ledger still matters.

This is why the movement of gold deserves more attention than the declarations of economists, politicians, central bankers, or global forums. The repatriation of gold is not fundamentally a commodity story, an inflation story, or even a monetary story. It is a custody story. It is a sovereignty story. It is an acknowledgment that possession remains the final court of appeal whenever confidence begins to wobble.

The irony is difficult to miss. At precisely the moment civilization celebrates digital currencies, tokenized assets, algorithmic settlement systems, cloud-based records, and increasingly abstract forms of ownership, many of the institutions responsible for preserving national wealth appear to be moving in the opposite direction. Public narratives race toward virtuality while institutional behavior quietly migrates toward physical custody. The speeches point toward digitization while the bullion trucks point toward reality.

Perhaps nowhere does this contradiction become more visible than when contemplating the fragility of the infrastructure upon which modern finance rests. We speak confidently of balances, portfolios, reserves, pensions, derivatives, and increasingly digital assets as though they possess an existence independent of the systems that record them. Yet the entire architecture rests upon a remarkably delicate foundation of electricity, communications, computation, synchronization, and trust. We have become so accustomed to continuity that we mistake continuity for permanence.

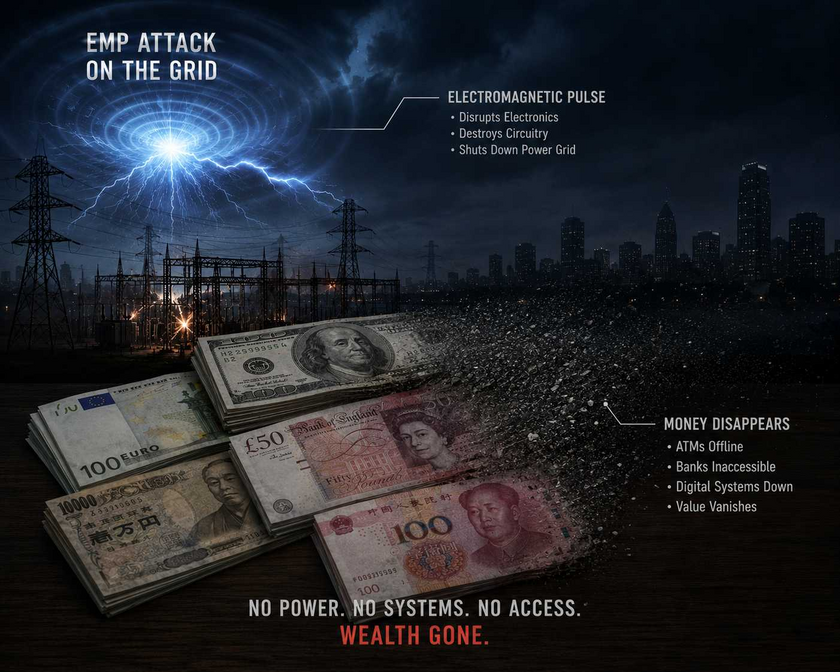
Consider not catastrophe but interruption. Consider a Carrington-scale solar event, a successful cyberattack, a cascading grid failure, or an electromagnetic pulse. The specific mechanism matters less than the principle. The lights go out. The servers stop responding. The networks cease synchronizing. The endless choreography of verification pauses. Legal claims may survive. Contracts may survive. Accounting entries may survive. Yet the practical ability to verify, transfer, access, or exercise those claims becomes uncertain. The abstractions remain theoretically intact while becoming functionally irrelevant.

Gold occupies a peculiar place within this thought experiment because it exists outside the thought experiment. It requires no password, no network connection, no authentication server, no intermediary, and no continuous electrical infrastructure to affirm its existence. The ledger may disappear. The gold remains. Whether one views gold as a monetary asset, a strategic reserve, or simply a historical curiosity, its persistence reveals something deeper about the nature of value itself. Assets that derive their existence from the systems that record them are fundamentally different from assets that exist independently of those systems.

What fascinates me, however, is not the rhetoric surrounding the so-called Great Reset, because the phrase itself has become one of the most effective distractions of the modern era. During the COVID years, populations were conditioned into increasingly reflexive forms of polarization in which every issue was immediately translated into opposing camps, every observation became a declaration of allegiance, and every question became a test of ideological loyalty. One side treated the Great Reset as evidence of a coordinated conspiracy while the other dismissed it as evidence of irrational paranoia. Both reactions produced the same outcome. Attention became fixed upon the slogan while remaining safely distant from the structure beneath it.

History has never required a committee to produce a reset. Resets emerge whenever claims become sufficiently detached from assets, whenever promises become sufficiently detached from productive capacity, whenever leverage becomes sufficiently detached from resilience, and whenever abstractions become sufficiently detached from reality. Long before a reset acquires a name, it exists as a tension embedded within the architecture itself.

This is why the most revealing actions in history are rarely the ones announced from podiums. They are the quiet movements that occur beneath the rhetoric. While populations argue over narratives, central banks move bullion. While commentators debate ideology, nations secure custody. While attention remains fixed upon political theater, the custodians of monetary power appear to be asking an older and more fundamental question concerning what survives when confidence falters, when access becomes uncertain, and when the systems responsible for recording ownership can no longer be assumed to function exactly as they did yesterday.

History repeatedly demonstrates that major transitions rarely emerge from the causes later assigned to them. Wars, sovereign defaults, financial crises, technological disruptions, infrastructure failures, and natural disasters frequently function as explanatory narratives that make visible contradictions that had already been accumulating for decades. The triggering event receives the blame because it is easier to understand than the architecture that rendered the event consequential. Yet the architecture is always where the real story resides. The event merely exposes what was already true.

Seen from this perspective, the most important question is not whether a particular organization intends to implement a Great Reset. The more important question concerns the conditions under which resets become inevitable. Whenever claims multiply faster than assets, whenever obligations expand faster than productive capacity, whenever financial abstractions drift sufficiently far from physical realities, tensions accumulate that eventually demand reconciliation. That reconciliation may arrive through inflation, restructuring, default, crisis, technological disruption, or events conveniently attributed to forces beyond human control, but the mechanism remains secondary to the principle. Reality eventually reasserts itself because reality is the only foundation upon which any abstraction can ultimately stand.

Viewed through that lens, the repatriation of gold appears less like a financial decision than an institutional acknowledgment that the distinction between claims and assets still matters. It represents a quiet recognition that resilience and possession acquire increasing importance precisely when complexity and uncertainty begin to rise. It suggests that beneath the public narratives, beneath the political theater, and beneath the endless distractions that dominate contemporary discourse, some of the world's most consequential actors may be asking the same question that inspired an essay sixteen years ago. What do you actually possess when the systems recording possession become uncertain?

The question is not fundamentally about gold. It is not fundamentally about vaults. It is not fundamentally about central banks. It is a question about the difference between a thing and a description of a thing, between ownership and access, between claims and assets, between abstractions and realities. It is the question that emerges whenever a civilization becomes sufficiently dependent upon representations that it forgets to examine the realities those representations are intended to describe.

Sixteen years ago I asked what was in your wallet. Watching nations quietly move bullion across oceans and into sovereign custody, the question feels sharper today than it did then. Not because the answer has changed, but because the institutions themselves appear increasingly unwilling to pretend that a claim and an asset are the same thing. The distinction sounded eccentric in 2010. It sounds increasingly obvious in 2026. The most interesting question is whether the rest of us will recognize the significance of that realization before history once again forces the issue on its own terms.

Source

🙏To support my work, Helping to keep the signal high and the noise low:

👉 Cashapp: $thedinarian

👉 Buy me a coffee: https://buymeacoffee.com/thedinarian

👉 PayPal: Scan the QR code below 📲 or Click Here: 

👇 Crypto Donations 👇

XRP: r9pid4yrQgs6XSFWhMZ8NkxW3gkydWNyQX
XLM: GDMJF2OCHN3NNNX4T4F6POPBTXK23GTNSNQWUMIVKESTHMQM7XDYAIZT
XDC: xdcc2C02203C4f91375889d7AfADB09E207Edf809A6

Read full Article
post photo preview
⚠️90 DAYS WITHOUT THE GRID⚠️
Why Governments Are Preparing for Critical Systems to Fail

MIND BEND THEORY | DOCUMENTED INVESTIGATION

The United States is preparing major military installations to continue operating if civilian infrastructure goes down. Britain is telling households to prepare for days without essential services. India is warning that an attack on the financial system can weaken a nation. And the Bank of England is asking what happens when cyber defenses fail—not if they can prevent every attack.

Individually, each development has an explanation.

Put them beside one another, however, and a larger pattern becomes visible.

Over the span of only a few weeks, governments and financial authorities in the United States, United Kingdom and India have publicly discussed preparations for disruptions involving some of the systems modern society depends upon most:

Power.

Water.

Fuel.

Communications.

Banking.

Supply chains.

This does not establish that these governments are preparing for one secret event.

There is no public evidence of a coordinated countdown, predetermined blackout date or single intelligence warning connecting them.

But there is something here that can be documented.

Governments are increasingly planning around a question that sounds very different from traditional emergency preparedness:

What happens when the systems we normally assume will be available are no longer available?

And in the United States, that question has now reached the Pentagon.

DOCUMENT 01

UNITED STATES — FORTRESS AMERICA

On September 30, 2026, Defense Secretary Pete Hegseth established a program called FORTRESS America.

The acronym stands for:

Federal Operations for Resilience, Troop Resources, Energy, Supply and Survivability.

The program addresses a vulnerability that rarely receives much public attention:

The world's most powerful military still depends extensively on civilian infrastructure.

Electric grids.

Commercial supply chains.

Communications infrastructure.

Fuel.

Foreign sources of critical materials.

FORTRESS America is intended to reduce those dependencies.

The Pentagon's own public description says the initiative is designed to ensure that major U.S. military installations generate independent power so that bases remain operational even if the civilian grid is taken down by cyberattack or sabotage.

It goes beyond electricity.

The program includes five major areas:

Energy independence

Installation hardening and cyber resilience

Supply-chain and defense-industrial-base resilience

Strategic defense reserves

Space and spectrum resilience

The Pentagon also wants deeper reserves of critical supplies so military operations can continue when ordinary supply lines are disrupted.

The underlying idea is simple:

The military should be capable of functioning even when the infrastructure surrounding it cannot.

An October 7 implementation memorandum obtained by DefenseScoop shows that the Pentagon had already begun establishing the FORTRESS America Program Office and assigning officials to implement those objectives.

Then another piece of the story emerged.

DOCUMENT 02

THE 90-DAY REQUIREMENT

On October 25, Fox News published details from additional FORTRESS America documents its reporters reviewed.

According to that reporting, major continental U.S. military installations are being prepared to sustain essential operations for at least 90 days without outside support.

The essential systems reportedly include:

Power.

Water.

Fuel.

Communications.

Think about the distinction carefully.

The Pentagon isn't telling Americans that the United States will lose electricity for 90 days.

It isn't predicting a 90-day blackout.

Military contingency planning deliberately prepares for scenarios officials hope never occur.

But preparing installations for this possibility tells us something about the scenario being considered.

The Pentagon is building resilience around the possibility that a sufficiently serious conflict or attack could interfere with the civilian systems on which military installations normally depend.

The publicly released FORTRESS material specifically discusses:

Cyberattack.

Sabotage.

Grid disruption.

Foreign supply-chain disruption.

Attacks against installations.

And prolonged military contingencies.

That makes the 90-day requirement significant—but it must be described accurately.

Mind Bend Theory verification note:

The September 30 FORTRESS America program itself is documented publicly.

The October 7 implementation memorandum has been reported and described by DefenseScoop.

The 90-day requirement, however, currently comes from documents reviewed by Fox News, rather than a primary 90-day document independently published for the public.

That distinction matters.

We follow the documents as far as they take us—and no farther.

DOCUMENT 03

UNITED KINGDOM — BE READY FOR THREE DAYS

Now cross the Atlantic.

On October 22, the British government launched its new Be Ready campaign.

This time the audience wasn't the military.

It was ordinary households.

The UK government is asking households that are able to do so to prepare to remain self-sufficient for approximately three days during an emergency.

The government specifically discusses disruptions affecting:

Power.

Water.

Phones.

Internet access.

A Parliamentary Written Statement issued the same day explicitly states:

“The updated advice calls on households to be self-sufficient for three days in the case of an emergency.”

The government recommends maintaining three days of bottled water and non-perishable food.

Its expanded preparedness guidance includes:

Approximately three litres of drinking water per person per day

Three days of non-perishable food

Battery-powered or wind-up radio

Torch and spare batteries

Charged power bank

Essential medications

First-aid supplies

Blankets and warm clothing

Important telephone numbers written down

Basic hygiene supplies

Cash

Why cash?

Because during some disruptions, electronic payment systems and ATMs may not function normally.

That creates an important connection between infrastructure and finance.

Electricity isn't isolated from banking.

Communications aren't isolated from payments.

Modern infrastructure is interconnected.

And failure can move through those connections.

DOCUMENT 04

INDIA — “WARS ARE NOT FOUGHT WITH WEAPONS ALONE”

Three days later, on October 25, another statement appeared.

This one came from Indian Prime Minister Narendra Modi.

Modi was inaugurating the Reserve Bank of India's newly established Data Centre and Cybersecurity Training Institute in Bhubaneswar.

The facilities are designed to strengthen the technological foundations and cybersecurity resilience of India's financial system.

Four data centres will host mission-critical payment and settlement systems.

But Modi's explanation of why this matters went beyond ordinary cybersecurity.

His official statement says:

“Nowadays, wars are not fought with weapons alone; a nation can also be weakened by attacking its economy.”

He continued by saying India's growing economy requires its banking system to be protected against cyber looters and cyber terrorists.

That puts another critical system into the picture:

Money.

A modern economy depends on digital banking infrastructure almost as heavily as it depends on electricity and telecommunications.

Payment systems move commerce.

Banks hold liquidity.

Settlement systems move money between financial institutions.

Data centres keep those networks functioning.

Disrupt the financial infrastructure badly enough and the consequences don't remain inside banks.

They reach businesses.

Supply chains.

Payroll.

Purchasing.

Markets.

And households.

DOCUMENT 05

BANK OF ENGLAND — WHAT IF CYBER DEFENSE FAILS?

There is another document worth reading.

On June 30, Bank of England Deputy Governor Sarah Breeden delivered a speech titled:

“Agents of Change.”

The subject was artificial intelligence and financial stability.

One section deserves particular attention.

Breeden warned that advanced AI systems are becoming increasingly capable of identifying and chaining together cyber vulnerabilities.

That changes the nature of cyber risk.

AI can help defenders.

But the same capabilities can potentially increase the speed and effectiveness of attackers.

The important change in thinking comes afterward.

Preventing attacks is no longer enough.

Financial institutions must also prepare to recover after a successful attack.

Breeden raised the possibility of simultaneous disruption across multiple financial firms.

She then asked whether critical financial institutions may eventually require completely separate failover capabilities—or even the ability to rebuild compromised core systems from “bare metal.”

In October, Reuters reported that the Bank of England was pushing financial institutions further toward this type of recovery planning.

That represents a subtle but significant change in the question.

It isn't simply:

How do we stop the attack?

It's becoming:

What happens if we don't?

And:

How do we keep the system functioning afterward?

CONNECT THE DOCUMENTS

Now put the documents beside one another.

UNITED STATES

Military installations are being hardened so essential operations can continue when civilian infrastructure is disrupted.

UNITED KINGDOM

Households are being told to prepare for three days without services they normally assume will remain available.

INDIA

The prime minister publicly warns that modern conflict can weaken a country by attacking its economy and calls for stronger protection of banking infrastructure.

BANK OF ENGLAND

Financial authorities are examining recovery scenarios in which cyber defenses have already failed and multiple institutions could potentially be disrupted simultaneously.

These aren't identical programs.

They aren't even aimed at the same people.

And there is currently no public evidence demonstrating that they were coordinated.

But they share one important assumption:

CRITICAL SYSTEMS CAN FAIL.

And resilience therefore cannot begin after the failure occurs.

It has to exist beforehand.

THE SYSTEM BEHIND THE SYSTEM

This is where the story becomes bigger than individual announcements.

Modern infrastructure isn't a collection of isolated systems.

It's a network.

Consider what happens when electricity fails.

Without power, telecommunications eventually become difficult to maintain.

Without communications, electronic payments can be affected.

Fuel pumps require electricity.

Water systems depend on pumping and treatment infrastructure.

Businesses depend on payment processing.

Supply chains depend on communications, transportation and fuel.

Hospitals require electricity, communications, water, medicine and logistics simultaneously.

A serious disruption doesn't necessarily remain inside the system where it started.

It can propagate.

POWER → COMMUNICATIONS → BANKING → COMMERCE → SUPPLY CHAINS

And the dependency runs in multiple directions.

That interconnectedness is precisely why governments plan for resilience.

WHAT THIS DOES NOT PROVE

Mind Bend Theory exists to examine unusual patterns.

But a pattern isn't automatically proof of a conspiracy.

There is currently no public evidence showing that Washington, London and New Delhi are secretly preparing for the same scheduled event.

There is no verified date for a coming global blackout.

There is no public document establishing an imminent 90-day collapse of the American electrical grid.

And the Pentagon's 90-day military resilience requirement should not be interpreted as a prediction that Americans will lose electricity for 90 days.

That would go beyond the evidence.

What the evidence actually establishes is interesting enough.

Governments increasingly consider disruption of power, communications, supply chains and financial infrastructure plausible enough to justify concrete preparation.

The UK is preparing households.

The United States is hardening military infrastructure.

India is strengthening the technological backbone of its financial system.

The Bank of England is thinking about how banks recover after cyber defenses fail.

That isn't speculation.

It's in the documents.

THE QUESTION

Perhaps the most important change isn't what governments believe will happen.

It's what they're preparing to survive.

For decades, infrastructure security focused heavily on preventing failure.

The emerging model looks different:

Assume something eventually gets through.

Assume something eventually goes down.

Build the ability to continue operating anyway.

The Pentagon calls that resilience.

The UK calls it being ready.

Central banks call it operational resilience.

Different terminology.

Same fundamental question:

WHAT STILL WORKS WHEN THE SYSTEM DOESN'T?

DOCUMENT TRAIL

Read the Evidence Yourself

Mind Bend Theory strongly encourages readers to examine the original material rather than relying solely on our interpretation.

🇺🇸 DOCUMENT 01 — FORTRESS America Establishment

September 30, 2026

Defense Secretary Pete Hegseth's memorandum establishes FORTRESS America as a Department of Defense resilience program.

The publicly reported memorandum establishes the program around installation resilience, independent energy, strategic reserves, supply chains and related national-defense infrastructure.

Source type: Pentagon memorandum / official announcement.

🇺🇸 DOCUMENT 02 — FORTRESS America Implementation Memorandum

October 7, 2026

DefenseScoop obtained the memorandum from Under Secretary for Acquisition and Sustainment Michael Duffey directing officials to begin operationalizing the FORTRESS America Program Office.

It identifies five foundational pillars, including energy independence, installation hardening and cyber resilience, strategic reserves and supply-chain resilience.

Source type: Pentagon memorandum obtained by DefenseScoop.

🇺🇸 DOCUMENT 03 — 90-Day FORTRESS Requirement

October 25, 2026

Fox News reports that documents it reviewed require major continental U.S. installations to sustain essential operations for at least 90 days without outside support.

Source type: Journalistic reporting based on documents reviewed by reporters.

Important: This is not currently being presented by Mind Bend Theory as a publicly released primary 90-day Pentagon document.

🇬🇧 DOCUMENT 04 — UK Cabinet Office Be Ready Announcement

October 22, 2026

The Cabinet Office announces the three-year Be Ready campaign and describes preparation for disruption affecting power, water, phones and internet.

Source type: Official UK government publication.

🇬🇧 DOCUMENT 05 — Parliamentary Written Statement HCWS409

October 22, 2026

The UK Parliament records the government's explicit recommendation that households prepare to remain self-sufficient for three days.

Source type: Official Parliamentary record.

🇬🇧 DOCUMENT 06 — Be Ready Household Emergency Checklist

The government's practical household guidance provides recommendations for water, food, radio, lighting, medication, power banks, emergency cash and other supplies.

Source type: Official UK government preparedness guidance.

🇮🇳 DOCUMENT 07 — Prime Minister of India / RBI Cybersecurity Facilities

October 25, 2026

Official statement documenting the opening of the Reserve Bank of India's Data Centre and Cybersecurity Training Institute and Modi's warning that countries can be weakened through attacks against their economies.

Source type: Official Government of India statement.

🇬🇧 DOCUMENT 08 — “Agents of Change” — Sarah Breeden

June 30, 2026

The Bank of England deputy governor discusses rapidly advancing AI cyber capabilities, simultaneous disruption across financial institutions, separate failover infrastructure and potentially rebuilding compromised systems from bare metal.

Source type: Official Bank of England speech.

DOCUMENT 09 — Bank of England Cyber-Recovery Reporting

October 15, 2026

Reuters reports on the Bank of England's push for stronger recovery capabilities against AI-enabled cyberattacks, including bare-metal recovery.

Source type: Independent reporting.

MIND BEND THEORY

Follow the documents. Separate what they prove from what they don't.

Then ask why the preparation is happening now.

Documents attached to the investigation

FORTRESS America — Sept. 30 memorandum record
Pentagon FORTRESS America implementation memorandum — DefenseScoop
FORTRESS America 90-day documents — Fox News investigation
UK Cabinet Office — Be Ready announcement
UK Parliament — Written Statement HCWS409
India PM's Office — RBI Data Centre & Cybersecurity Training Institute
Bank of England — Sarah Breeden, “Agents of Change”
Reuters — Bank of England cyber-recovery warning

Source

🙏To support my work, Helping to keep the signal high and the noise low:

👉 Cashapp: $thedinarian

👉 Buy me a coffee: https://buymeacoffee.com/thedinarian

👉 PayPal: Scan the QR code below 📲 or Click Here: 

👇 Crypto Donations 👇

XRP: r9pid4yrQgs6XSFWhMZ8NkxW3gkydWNyQX
XLM: GDMJF2OCHN3NNNX4T4F6POPBTXK23GTNSNQWUMIVKESTHMQM7XDYAIZT
XDC: xdcc2C02203C4f91375889d7AfADB09E207Edf809A6

Read full Article
September 13, 2026
post photo preview
Revolut Leak Shows the Cost of Constant ID Collection
Revolut’s mistake is the news, but the bigger problem is the growing number of companies being encouraged or required to keep copies of our most sensitive identity documents.

Online bank Revolut has revealed that it gave out sensitive personal and financial information of an undisclosed number of its customers in response to a fake government request.

The information that was handed over to an “unauthorized third party” reportedly includes names, dates of birth, occupations, addresses, phone numbers, account numbers, transaction histories (including Bitcoin), and even copies of government-issued IDs and onboarding verification selfies.

Revolut claims that derived biometric face data was not.

The company said that the data was handed over in response to an email that came from a real government agency’s domain, but was not actually sent or authorized by that agency.

The email passed several authentication checks (SPF, DKIM, and DMARC) that are designed to establish the authenticity of a message’s origin and integrity, but do not verify the legitimacy of the legal request itself.

Revolut said that it complied with the request “under the reasonable belief that it was an authentic government agency request” – and only later found out that it was not.

Revolut said it later realized its mistake, blocked the email address, and reported the incident to the relevant authorities.

Revolut said that only a “limited” number of its customers were affected by the data leak, and that the company’s systems were not hacked, nor was any money stolen.

The story broke on September 11 when Revolut customers started receiving an email notice about a data leak, and the news was picked up by media outlets the following day.

Revolut notice explaining customer identity and financial data was shared after an unauthorized government email request.

The reason this is a recurring problem is that companies are keeping highly sensitive information about their customers’ identities, and sometimes even financial transactions, for a long time, and this data is then available to be disclosed to third parties – either in response to valid legal requests, or, as in the case of Revolut, fake ones.

One reason for this is know your customer (KYC) and anti-money laundering (AML) rules. Revolut’s current UK customer privacy notice spells it out: the company generally keeps personal data of UK customers for no more than seven years after the relationship ends, and sometimes longer – for legal reasons.

This means that even if you close your account, your identity documents don’t disappear.

And while the incident with Revolut happened in the financial sector, it’s by no means the only one that requires customers to hand over sensitive identity information. Discord, a popular chat service, said in an October 9, 2025 security update that government ID photos of approximately 70,000 users may have been exposed after a third-party customer service provider got hacked.

This was not a financial service, nor the same type of attack. But the result was similar – because the underlying business process was the same: requiring and storing sensitive identity documents. In the case of Discord, these were used to review age-related appeals.

It’s hard to do anything about a copy of your old passport, or a photo of your face, or a record of your past transactions. These can be used to identify and profile you, and can be used to carry out targeted fraud. And this can happen even if the initial disclosure didn’t result in financial loss.

The more companies are forced to collect and store such information, and the more of it they have, the more opportunities there are for this data to be leaked, either by the company itself or a third party it works with. That's what makes governments' push for more ID checks just to access ordinary parts of life so reckless.

Source

🙏To support my work, Helping to keep the signal high and the noise low:

👉 Cashapp: $thedinarian

👉 Buy me a coffee: https://buymeacoffee.com/thedinarian

👉 PayPal: Scan the QR code below 📲 or Click Here: 

👇 Crypto Donations 👇

XRP: r9pid4yrQgs6XSFWhMZ8NkxW3gkydWNyQX
XLM: GDMJF2OCHN3NNNX4T4F6POPBTXK23GTNSNQWUMIVKESTHMQM7XDYAIZT
XDC: xdcc2C02203C4f91375889d7AfADB09E207Edf809A6

Read full Article
See More
Available on mobile and TV devices
google store google store app store app store
google store google store app tv store app tv store amazon store amazon store roku store roku store
Powered by Locals