Dinarian888
News • Business • Investing & Finance
The Society for Worldwide Interbank Financial Telecommunication (Swift)
What is it actually?
November 22, 2023
post photo preview

This is a great amount of information and history regarding S.W.I.F.T, and sums up why THEY are moving to the ISO standards worldwide. 

Knowledge Is Power ~D

The Society for Worldwide Interbank Financial Telecommunication (Swift), legally S.W.I.F.T. SC, is a Belgian cooperative society providing services related to the execution of financial transactions and payments between certain banks worldwide. Its principal function is to serve as the main messaging network through which international payments are initiated.[2] It also sells software and services to financial institutions, mostly for use on its proprietary "SWIFTNet", and assigns ISO 9362 Business Identifier Codes (BICs), popularly known as "Swift codes".

The Swift messaging network is a component of the global payments system.[3] Swift acts as a carrier of the "messages containing the payment instructions between financial institutions involved in a transaction".[4][5] However, the organisation does not manage accounts on behalf of individuals or financial institutions, and it does not hold funds from third parties.[6] It also does not perform clearing or settlement functions.[7][5] After a payment has been initiated, it must be settled through a payment system, such as TARGET2 in Europe.[8] In the context of cross-border transactions, this step often takes place through correspondent banking accounts that financial institutions have with each other.[4]

As of 2018, around half of all high-value cross-border payments worldwide used the Swift network,[9] and in 2015, Swift linked more than 11,000 financial institutions in over 200 countries and territories, who were exchanging an average of over 32 million messages per day (compared to an average of 2.4 million daily messages in 1995).[10]

Though widely utilised, Swift has been criticised for its inefficiency. In 2018, the London-based Financial Times noted that transfers frequently "pass through multiple banks before reaching their final destination, making them time-consuming, costly and lacking transparency on how much money will arrive at the other end".[9] Swift has since introduced an improved service called "Global Payments Innovation" (GPI), claiming it was adopted by 165 banks and was completing half its payments within 30 minutes.[9] The new standard which included Swift Go was supposed to be utilised in receiving and transferring low-value international payments. One of the significant changes was the transaction amount, which would not differ from start to the end. However, as of 2023, uptake was mixed. For instance, Alisherov Eraj, Alif Bank Treasury Department Swift Transfers & Banking Relationship Expert in the Republic of Tajikistan, describes that the leading cause for the late Swift Go adoption in Tajikistan was the Core Banking System itself. To connect to Swift Go, he adds, banking system interfaces needed to be upgraded and integrate with their software to be fully compatible, this hindered many banks from adopting the technology earlier.

As a cooperative society under Belgian law, Swift is owned by its member financial institutions. It is headquartered in La Hulpe, Belgium, near Brussels; its main building was designed by Ricardo Bofill Taller de Arquitectura and completed in 1989.[11] The chairman of Swift is Graeme Munro of United Kingdom,[12] and its CEO is Javier Pérez-Tasso of Spain.[13] Swift hosts an annual conference, called Sibos, specifically aimed at the financial services industry.[14]

History[edit]

SWIFT was founded in Brussels on 3 May 1973 under the leadership of its inaugural Swedish CEO, Carl Reuterskiöld (1973–1989), a Wallenberg-associate, and was supported by 239 banks in 15 countries.[15] Before its establishment, international financial transactions were communicated over Telex, a public system involving manual writing and reading of messages.[16] It was set up out of fear of what might happen if a single private and fully American entity controlled global financial flows – which before was First National City Bank (FNCB) of New York – later Citibank. In response to FNCB's protocol, FNCB's competitors in the US and Europe pushed an alternative "messaging system that could replace the public providers and speed up the payment process".[17] SWIFT started to establish common standards for financial transactions and a shared data processing system and worldwide communications network designed by Logica and developed by the Burroughs Corporation.[18] Fundamental operating procedures and rules for liability were established in 1975, and the first message was sent in 1977. SWIFT's first international (non-European) operations centre was inaugurated by Governor John N. Dalton of Virginia in 1979.[19]

Standards[edit]

SWIFT has become the industry standard for syntax in financial messages. Messages formatted to SWIFT standards can be read and processed by many well-known financial processing systems, whether or not the message travelled over the SWIFT network. SWIFT cooperates with international organizations for defining standards for message format and content. SWIFT is also Registration authority (RA) for the following ISO standards: [20]

  • ISO 9362: 1994 Banking – Banking telecommunication messages – Bank identifier codes
  • ISO 10383: 2003 Securities and related financial instruments – Codes for exchanges and market identification (MIC)
  • ISO 13616: 2003 IBAN Registry
  • ISO 15022: 1999 Securities – Scheme for messages (Data Field Dictionary) (replaces ISO 7775)
  • ISO 20022-1: 2004 and ISO 20022-2:2007 Financial services – Universal Financial Industry message scheme

In RFC 3615 urn:swift: was defined as Uniform Resource Names (URNs) for SWIFT FIN.[21]

Operations centres[edit]

The SWIFT secure messaging network is run from three data centres, located in the United States, the Netherlands, and Switzerland. These centres share information in near real-time. In case of a failure in one of the data centres, another is able to handle the traffic of the complete network(Sound familiar? "Nodes"). SWIFT uses submarine communications cables to transmit its data.[22]

Shortly after opening its third data centre in Switzerland in 2009,[23] SWIFT introduced new distributed architecture with two messaging zones, European and Trans-Atlantic, so data from European SWIFT members no longer mirrored the U.S. data centre.[24] European zone messages are stored in the Netherlands and in part of the Swiss operating centre; Trans-Atlantic zone messages are stored in the United States and in another part of the Swiss operating centre that is segregated from the European zone messages. Countries outside of Europe were by default allocated to the Trans-Atlantic zone, but could choose to have their messages stored in the European zone.

Data centres
SNSWIFT data centresType
1Zoeterwoude, NetherlandsOPC (Operating Centre)
2Culpeper, Virginia, United StatesOPC (Operating Centre)
3Diessenhofen, Switzerland[25]OPC (Operating Centre)
4Hong KongCommand and control


SWIFTNet network

SWIFT moved to its current IP network infrastructure, known as SWIFTNet, from 2001 to 2005,[26] providing a total replacement of the previous X.25 infrastructure. The process involved the development of new protocols that facilitate efficient messaging, using existing and new message standards. The adopted technology chosen to develop the protocols was XML, where it now provides a wrapper around all messages legacy or contemporary. The communication protocols can be broken down into:

InterAct

  • SWIFTNet InterAct Realtime
  • SWIFTNet InterAct Store and Forward

FileAct

  • SWIFTNet FileAct Realtime
  • SWIFTNet FileAct Store and Forward

Browse

  • SWIFTNet Browse


Architecture

SWIFT provides a centralized store-and-forward mechanism, with some transaction management. For bank A to send a message to bank B with a copy or authorization involving institution C, it formats the message according to standards and securely sends it to SWIFT. SWIFT guarantees its secure and reliable delivery to B after the appropriate action by C. SWIFT guarantees are based primarily on high redundancy of hardware, software, and people.


SWIFTNet Phase 2

During 2007 and 2008, the entire SWIFT network migrated its infrastructure to a new protocol called SWIFTNet Phase 2. The main difference between Phase 2 and the former arrangement is that Phase 2 requires banks connecting to the network to use a Relationship Management Application (RMA) instead of the former bilateral key exchange (BKE) system. According to SWIFT's public information database on the subject, RMA software should eventually prove more secure and easier to keep up-to-date; however, converting to the RMA system meant that thousands of banks around the world had to update their international payments systems to comply with the new standards. RMA completely replaced BKE on 1 January 2009.


Products and interfaces

SWIFT means several things in the financial world:

  1. a secure network for transmitting messages between financial institutions;
  2. a set of syntax standards for financial messages (for transmission over SWIFTNet or any other network)
  3. a set of connection software and services allowing financial institutions to transmit messages over SWIFT network.

Under 3 above, SWIFT provides turn-key solutions for members, consisting of linkage clients to facilitate connectivity to the SWIFT network and CBTs or "computer based terminals" which members use to manage the delivery and receipt of their messages. Some of the more well-known interfaces and CBTs provided to their members are:

  • SWIFTNet Link (SNL) software which is installed on the SWIFT customer's site and opens a connection to SWIFTNet. Other applications can only communicate with SWIFTNet through the SNL.
  • Alliance Gateway (SAG) software with interfaces (e.g., RAHA = Remote Access Host Adapter), allowing other software products to use the SNL to connect to SWIFTNet
  • Alliance WebStation (SAB) desktop interface for SWIFT Alliance Gateway with several usage options:
    1. administrative access to the SAG
    2. direct connection SWIFTNet by the SAG, to administrate SWIFT Certificates
    3. so-called Browse connection to SWIFTNet (also by SAG) to use additional services, for example Target2
  • Alliance Access (SAA) and Alliance Messaging Hub (AMH) are the main messaging software applications by SWIFT, which allow message creation for FIN messages, routing and monitoring for FIN and MX messages. The main interfaces are FTA (files transfer automated, not FTP) and MQSA, a WebSphere MQ interface.
  • The Alliance Workstation (SAW) is the desktop software for administration, monitoring and FIN message creation. Since Alliance Access is not yet capable of creating MX messages, Alliance Messenger (SAM) has to be used for this purpose.
  • Alliance Web Platform (SWP) as new thin-client desktop interface provided as an alternative to existing Alliance WebStation, Alliance Workstation (soon)[when?] and Alliance Messenger.
  • Alliance Integrator built on Oracle's Java Caps which enables customer's back office applications to connect to Alliance Access or Alliance Entry.
  • Alliance Lite2 is a secure and reliable, cloud-based way to connect to the SWIFT network which is a light version of Alliance Access specifically targeting customers with low volume of traffic.


Services

There are four key areas that SWIFT services fall under in the financial marketplace: securities, treasury & derivatives, trade services. and payments-and-cash management.

Securities

  • SWIFTNet FIX (obsolete)
  • SWIFTNet Data Distribution
  • SWIFTNet Funds
  • SWIFTNet Accord for Securities (end of life October 2017)[27]

Treasury and derivatives

  • SWIFTNet Accord for Treasury (end of life October 2017)[27]
  • SWIFTNet Affirmations
  • SWIFTNet CLS Third Party Service

Cash management

  • SWIFTNet Bulk Payments
  • SWIFTNet Cash Reporting
  • SWIFTNet Exceptions and Investigations

Trade services


SWIFTREF

Swift Ref, the global payment reference data utility, is SWIFT's unique reference data service. Swift Ref sources data direct from data originators, including central banks, code issuers and banks making it easy for issuers and originators to maintain data regularly and thoroughly. SWIFTRef constantly validates and cross-checks data across the different data sets.[28]

SWIFTNet Mail[edit]

SWIFT offers a secure person-to-person messaging service, SWIFTNet Mail, which went live on 16 May 2007.[29] SWIFT clients can configure their existing email infrastructure to pass email messages through the highly secure and reliable SWIFTNet network instead of the open Internet. SWIFTNet Mail is intended for the secure transfer of sensitive business documents, such as invoices, contracts and signatories, and is designed to replace existing telex and courier services, as well as the transmission of security-sensitive data over the open Internet. Seven financial institutions, including HSBC, FirstRand Bank, Clearstream, DnB NOR, Nedbank, and Standard Bank of South Africa, as well as SWIFT piloted the service.[30]


U.S. government involvement

Terrorist Finance Tracking Program[edit]

A series of articles published on 23 June 2006 in The New York Times, The Wall Street Journal, and the Los Angeles Times revealed a program, named the Terrorist Finance Tracking Program, which the US Treasury Department, Central Intelligence Agency (CIA), and other United States governmental agencies initiated after the 11 September attacks to gain access to the SWIFT transaction database.[31]

After the publication of these articles, SWIFT quickly came under pressure for compromising the data privacy of its customers by allowing governments to gain access to sensitive personal information. In September 2006, the Belgian government declared that these SWIFT dealings with American governmental authorities were a breach of Belgian and European privacy laws.

In response, and to satisfy members' concerns about privacy, SWIFT began a process of improving its architecture by implementing a distributed architecture with a two-zone model for storing messages (see Operations centres).

Concurrently, the European Union negotiated an agreement with the United States government to permit the transfer of intra-EU SWIFT transaction information to the United States under certain circumstances. Because of concerns about its potential contents, the European Parliament adopted a position statement in September 2009, demanding to see the full text of the agreement and asking that it be fully compliant with EU privacy legislation, with oversight mechanisms emplaced to ensure that all data requests were handled appropriately.[32] An interim agreement was signed without European Parliamentary approval by the European Council on 30 November 2009,[33] the day before the Lisbon Treaty—which would have prohibited such an agreement from being signed under the terms of the codecision procedure—formally came into effect. While the interim agreement was scheduled to come into effect on 1 January 2010, the text of the agreement was classified as "EU Restricted" until translations could be provided in all EU languages and published on 25 January 2010.

On 11 February 2010, the European Parliament decided to reject the interim agreement between the EU and the US by 378 to 196 votes.[34][35] One week earlier, the parliament's civil liberties committee had already rejected the deal, citing legal reservations.[36]

In March 2011, it was reported that two mechanisms of data protection had failed: EUROPOL released a report complaining that requests for information from the US had been too vague (making it impossible to make judgments on validity)[37] and that the guaranteed right for European citizens to know whether their information had been accessed by US authorities had not been put into practice.[37]


Monitoring by the NSA

Der Spiegel reported in September 2013 that the National Security Agency (NSA) widely monitors banking transactions via SWIFT, as well as credit card transactions.[38] The NSA intercepted and retained data from the SWIFT network used by thousands of banks to securely send transaction information. SWIFT was named as a "target", according to documents leaked by Edward Snowden. The documents revealed that the NSA spied on SWIFT using a variety of methods, including reading "SWIFT printer traffic from numerous banks".[38] In April 2017, a group known as the Shadow Brokers released files allegedly from the NSA which indicate that the agency monitored financial transactions made through SWIFT.[39][40]


Use in sanctions:


Belarus

The European Union issued the first set of sanctions against Belarus - the first was introduced on 27 February 2022, which banned certain categories of Belarusian items in the EU, including timber, steel, mineral fuels and tobacco.[41] After the Lithuanian prime minister proposed disconnecting Belarus from SWIFT,[42] the European Union, which does not recognise Lukashenko as the legitimate President of Belarus, started to plan an extension of the sanctions already issued against Russian entities and top officials to its ally.[43]


Iran

In January 2012, the advocacy group United Against Nuclear Iran (UANI) implemented a campaign calling on SWIFT to end all relations with Iran's banking system, including the Central Bank of Iran. UANI asserted that Iran's membership in SWIFT violated US and EU financial sanctions against Iran as well as SWIFT's own corporate rules.[44]

Consequently, in February 2012, the U.S. Senate Banking Committee unanimously approved sanctions against SWIFT aimed at pressuring it to terminate its ties with blacklisted Iranian banks. Expelling Iranian banks from SWIFT would potentially deny Iran access to billions of dollars in revenue using SWIFT but not from using IVTS. Mark Wallace, president of UANI, praised the Senate Banking Committee.[45]

Initially SWIFT denied that it was acting illegally,[45] but later[when?] said that "it is working with U.S. and European governments to address their concerns that its financial services are being used by Iran to avoid sanctions and conduct illicit business".[46] Targeted banks would be—amongst others—Saderat Bank of Iran, Bank Mellat, Post Bank of Iran and Sepah Bank.[47] On 17 March 2012, following agreement two days earlier between all 27 member states of the Council of the European Union and the Council's subsequent ruling, SWIFT disconnected all Iranian banks that had been identified as institutions in breach of current EU sanctions from its international network and warned that even more Iranian financial institutions could be disconnected from the network.

In February 2016, most Iranian banks reconnected to the network following the lift of sanctions due to the Joint Comprehensive Plan of Action.[48]


Russia

Similarly, in August 2014 the UK planned to press the EU to block Russian use of SWIFT as a sanction due to Russian military intervention in Ukraine.[49] However, SWIFT refused to do so.[50] SPFS, a Russian alternative to SWIFT, was developed by the Central Bank of Russia as a backup measure.[51]

During the prelude to the 2022 Russian invasion of Ukraine, the United States developed preliminary possible sanctions against Russia, but excluded banning Russia from SWIFT.[52] Following the 2022 Russian invasion of Ukraine, the foreign ministers of the Baltic states Lithuania, Latvia, and Estonia called for Russia to be cut off from SWIFT. However, other EU member states were reluctant, both because European lenders held most of the nearly $30 billion in foreign banks' exposure to Russia and because Russia had developed the SPFS alternative.[53] The European Union, United Kingdom, Canada, and the United States finally agreed to remove few Russian banks from the SWIFT messaging system in response to the 2022 Russian invasion of Ukraine; the governments of France, Germany, Italy and Japan individually released statements alongside the EU.[54][5]

On 20 March 2023, the Russian Federation banned the use of SWIFT.[55][56]


Israel

In 2014, SWIFT rejected calls from pro-Palestinian activists to revoke Israeli banks' access to its network owing to the Israeli occupation of Palestinian territory.[57]


Competitors

Alternatives to the SWIFT system include:

  1. CIPS: sponsored by China, for RMB related deals. 1467 financial institutions in 111 countries and regions have connected to the system. The actual business covers more than 4,200 banking institutions in 182 countries and regions around the world.[58][59][60]
  2. SFMS: sponsored by India
  3. SPFS: developed by the Russian Federation[61]
  4. INSTEX: sponsored by the European Union, limited to non-USD transactions for trade with Iran, largely unused and ineffective[62][63]


Security

In 2016 an $81 million theft from the Bangladesh central bank via its account at the New York Federal Reserve Bank was traced to hacker penetration of SWIFT's Alliance Access software, according to a New York Times report. It was not the first such attempt, the society acknowledged, and the security of the transfer system was undergoing new examination accordingly.[64] Soon after the reports of the theft from the Bangladesh central bank, a second, apparently related, attack was reported to have occurred on a commercial bank in Vietnam.[65][66]

Both attacks involved malware written to both issue unauthorized SWIFT messages and to conceal that the messages had been sent. After the malware sent the SWIFT messages that stole the funds, it deleted the database record of the transfers then took further steps to prevent confirmation messages from revealing the theft. In the Bangladeshi case, the confirmation messages would have appeared on a paper report; the malware altered the paper reports when they were sent to the printer. In the second case, the bank used a PDF report; the malware altered the PDF viewer to hide the transfers.[65]

In May 2016, Banco del Austro (BDA) in Ecuador sued Wells Fargo after Wells Fargo honoured $12 million in fund transfer requests that had been placed by thieves.[66] In this case, the thieves sent SWIFT messages that resembled recently cancelled transfer requests from BDA, with slightly altered amounts; the reports do not detail how the thieves gained access to send the SWIFT messages. BDA asserts that Wells Fargo should have detected the suspicious SWIFT messages, which were placed outside of normal BDA working hours and were of an unusual size. Wells Fargo claims that BDA is responsible for the loss, as the thieves gained access to the legitimate SWIFT credentials of a BDA employee and sent fully authenticated SWIFT messages.[66]

In the first half of 2016, an anonymous Ukrainian bank and others—even "dozens" that are not being made public—were variously reported to have been "compromised" through the SWIFT network and to have lost money.[67]

In March 2022, Swiss newspaper Neue Zürcher Zeitung reported about the increased security precautions by the State Police of Thurgau at the SWIFT data centre in Diessenhofen. After most of the Russian banks have been excluded from the private payment system, the risk of sabotage was considered higher. Inhabitants of the town described the large complex as a "fortress" or "prison" where frequent security checks of the fenced property are conducted.[68]
Link

community logo
Join the Dinarian888 Community
To read more articles like this, sign up and join my community today
0
What else you may like…
Videos
Podcasts
Posts
Articles
September 26, 2026
The true enemy of peace is NOT Russia, China, or Iran…

“The Rothschilds claim to be Jewish, but are actually Khazars from Mongolian Eastern Europe…”

The true enemy of peace is the Rothschild-Khazarian Mafia!

Forbidden Knowledge 📚

00:02:55
September 26, 2026
Just as Guns Don't Kill People...

🚨 BIG NEWS: Speaking to a packed room of over 1,000 attendees at ETH Zurich, Edward Snowden called for Sam Altman to face IMPRISONMENT to establish legal liability for harms caused by OpenAI's models—drawing massive, thunderous applause! 👏💥

Time to cut through the corporate "safetyism" PR distraction 🎭 and demand true accountability. Lock him up! 🔒🏛️

00:03:45
September 26, 2026
🚨 BREAKING: BlackRock lays off 600 employees, hitting the ESG division hardest. 📉💼

The global collapse of ESG is accelerating:

💸 $5 Trillion Lost: Global ESG investments have plummeted by $5 trillion in just 2 years as investors pull back.

⚖️ The Mechanism of Control: ESG has been used by massive institutional asset managers like BlackRock and Vanguard as a leverage system to force corporate alignment with social and political agendas.

🗣️ In Their Own Words: Watch BlackRock CEO Larry Fink (seated alongside the CEO of AmEx) explicitly explain how ESG metrics are deployed to "force behaviors" across the corporate landscape.

The narrative is crumbling, and the markets are responding in real time 🛑📉

00:00:29
🚨 Chutes is being framed as a Hyperliquid-style breakout for decentralized AI inference, with live revenue, verified GPU infrastructure, and a direct challenge to centralized cloud AI 🚨

Chutes is gaining attention as a decentralized AI inference platform that claims to combine real usage, cryptographic verification, confidential computing, and open-source infrastructure into a working production system. The thesis is simple: instead of trusting Big Tech clouds with AI workloads, users get a distributed compute layer built around verification and privacy.

🔑 Key points

🔹 Chutes is live in production and reportedly scaled to more than 1,170 active GPU nodes, including large numbers of Nvidia H200s and Blackwell-class hardware.

🔹 The platform says it has processed nearly 38 trillion tokens since launch across 53 deployed applications and more than 700,000 registered users.

🔹 The team reportedly cut unprofitable usage programs, reduced total token volume, and still improved revenue efficiency, with revenue per GPU rising sharply after removing subsidized traffic.

🔹 Chutes is using post-quantum cryptography, trusted execution environments, and Nvidia confidential ...

🚨 Chutes is being framed as a Hyperliquid-style breakout for decentralized AI inference, with live revenue, verified GPU infrastructure, and a direct challenge to centralized cloud AI 🚨
🚨 JPMorgan’s criticism of the CLARITY Act is fueling a fresh power struggle over who gets to write America’s crypto rules 🚨

A new clash is emerging between legacy finance and crypto legislation after JPMorgan CEO Jamie Dimon reportedly warned that the CLARITY Act could let crypto firms offer bank-like products without bank-level oversight. The dispute is quickly turning into a larger fight over regulation, competitiveness, and who controls the future architecture of digital finance in the United States.

🔑 Key points

🔹 Jamie Dimon reportedly called the CLARITY Act a threat to the financial system, arguing it could allow crypto firms to offer yield-like products while avoiding the capital, reserve, and oversight burdens traditional banks face.

🔹 Senator Cynthia Lummis pushed back publicly, framing the issue as a global strategic race and warning that if the U.S. does not set digital asset standards, other powers will.

🔹 The core tension is whether the bill creates legitimate regulatory clarity or simply opens the door to regulatory arbitrage for crypto platforms operating outside the traditional banking...

🚨 JPMorgan’s criticism of the CLARITY Act is fueling a fresh power struggle over who gets to write America’s crypto rules 🚨
👉 Coinbase just launched an AI agent for Crypto Trading

Custom AI assistants that print money in your sleep? 🔜

The future of Crypto x AI is about to go crazy.

👉 Here’s what you need to know:

💠 'Based Agent' enables creation of custom AI agents
💠 Users set up personalized agents in < 3 minutes
💠 Equipped w/ crypto wallet and on-chain functions
💠 Capable of completing trades, swaps, and staking
💠 Integrates with Coinbase’s SDK, OpenAI, & Replit

👉 What this means for the future of Crypto:

1. Open Access: Democratized access to advanced trading
2. Automated Txns: Complex trades + streamlined on-chain activity
3. AI Dominance: Est ~80% of crypto 👉txns done by AI agents by 2025

🚨 I personally wouldn't bet against Brian Armstrong and Jesse Pollak.

👉 Coinbase just launched an AI agent for Crypto Trading
Exit The System If You Have Not Already!

🏛 THE LAST WARNING BEFORE THE SHUTDOWN | James Rickards 🏛

​🏛️ Sovereign Debt & Monetary Debasement: Discusses the high national debt load in the United States (approaching $40 trillion) and argues that when debt-to-GDP ratios exceed sustainable levels, governments primarily manage sovereign obligations through currency debasement and inflation rather than explicit default.
​
🏦 Banking Plumbing & Systemic Leverage: Examines fractional reserve banking, shadow banking networks, and derivative exposure in commercial banks, referencing historical liquidity freezes such as the 1998 Long-Term Capital Management (LTCM) bailout and the 2008 financial crisis.

​🌐 Offshore Dollar Markets & Reserve Currency Realignment: Outlines the mechanics of the eurodollar market, shortages of high-grade repo collateral, and the consequences of freezing sovereign central bank foreign exchange reserves on global trust in reserve currencies.

​🌍 BRICS & Alternative Trade Settlement: Describes how ...

⚖️ SEC guidance gives Bittensor-style crypto economies more room to operate ⚖️

New SEC crypto-asset guidance distinguishes functioning networks from tokens sold mainly on promises of future development, creating clearer space for buybacks, burns, staking, and ongoing subnet economics.

🔑 Key points

🔹 Working networks receive clearer treatment: The SEC guidance separates functioning crypto systems from projects that depend primarily on managerial promises.

🔹 Buybacks are addressed: Treasury management, supply reduction, protocol-funded burns, and similar activities do not automatically turn a token into a securities offering when the underlying token is already treated as a non-security.

🔹 Bittensor’s burn economy fits the discussion: Manual subnet burns reportedly increased from 8 subnets to 17, while burned alpha grew from approximately 3,700 TAO worth to 6,600 TAO worth.

🔹 Revenue can support token economics: Subnets are increasingly using product revenue to buy back alpha, reduce supply, ...

Bittensors 2026 Exploit Summit Has Begun

Bittensor's Native Conference. September 28-29. 2026. New City Gas, Montreal, Canada. exploitsummit.com
○ Montreal

Watch it live: https://stream.vidaio.io/?event=4f67b49580a44edd996dcece7e10b490

post photo preview
September 13, 2026
post photo preview
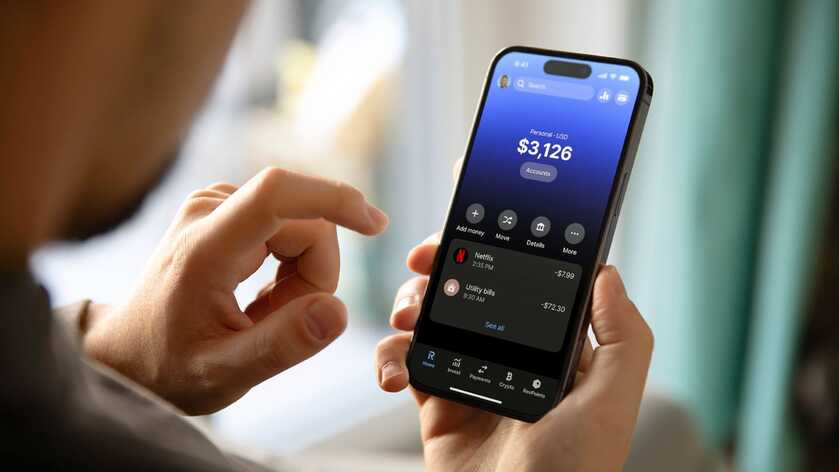
Revolut Leak Shows the Cost of Constant ID Collection
Revolut’s mistake is the news, but the bigger problem is the growing number of companies being encouraged or required to keep copies of our most sensitive identity documents.

Online bank Revolut has revealed that it gave out sensitive personal and financial information of an undisclosed number of its customers in response to a fake government request.

The information that was handed over to an “unauthorized third party” reportedly includes names, dates of birth, occupations, addresses, phone numbers, account numbers, transaction histories (including Bitcoin), and even copies of government-issued IDs and onboarding verification selfies.

Revolut claims that derived biometric face data was not.

The company said that the data was handed over in response to an email that came from a real government agency’s domain, but was not actually sent or authorized by that agency.

The email passed several authentication checks (SPF, DKIM, and DMARC) that are designed to establish the authenticity of a message’s origin and integrity, but do not verify the legitimacy of the legal request itself.

Revolut said that it complied with the request “under the reasonable belief that it was an authentic government agency request” – and only later found out that it was not.

Revolut said it later realized its mistake, blocked the email address, and reported the incident to the relevant authorities.

Revolut said that only a “limited” number of its customers were affected by the data leak, and that the company’s systems were not hacked, nor was any money stolen.

The story broke on September 11 when Revolut customers started receiving an email notice about a data leak, and the news was picked up by media outlets the following day.

Revolut notice explaining customer identity and financial data was shared after an unauthorized government email request.

The reason this is a recurring problem is that companies are keeping highly sensitive information about their customers’ identities, and sometimes even financial transactions, for a long time, and this data is then available to be disclosed to third parties – either in response to valid legal requests, or, as in the case of Revolut, fake ones.

One reason for this is know your customer (KYC) and anti-money laundering (AML) rules. Revolut’s current UK customer privacy notice spells it out: the company generally keeps personal data of UK customers for no more than seven years after the relationship ends, and sometimes longer – for legal reasons.

This means that even if you close your account, your identity documents don’t disappear.

And while the incident with Revolut happened in the financial sector, it’s by no means the only one that requires customers to hand over sensitive identity information. Discord, a popular chat service, said in an October 9, 2025 security update that government ID photos of approximately 70,000 users may have been exposed after a third-party customer service provider got hacked.

This was not a financial service, nor the same type of attack. But the result was similar – because the underlying business process was the same: requiring and storing sensitive identity documents. In the case of Discord, these were used to review age-related appeals.

It’s hard to do anything about a copy of your old passport, or a photo of your face, or a record of your past transactions. These can be used to identify and profile you, and can be used to carry out targeted fraud. And this can happen even if the initial disclosure didn’t result in financial loss.

The more companies are forced to collect and store such information, and the more of it they have, the more opportunities there are for this data to be leaked, either by the company itself or a third party it works with. That's what makes governments' push for more ID checks just to access ordinary parts of life so reckless.

Source

🙏To support my work, Helping to keep the signal high and the noise low:

👉 Cashapp: $thedinarian

👉 Buy me a coffee: https://buymeacoffee.com/thedinarian

👉 PayPal: Scan the QR code below 📲 or Click Here: 

👇 Crypto Donations 👇

XRP: r9pid4yrQgs6XSFWhMZ8NkxW3gkydWNyQX
XLM: GDMJF2OCHN3NNNX4T4F6POPBTXK23GTNSNQWUMIVKESTHMQM7XDYAIZT
XDC: xdcc2C02203C4f91375889d7AfADB09E207Edf809A6

Read full Article
post photo preview
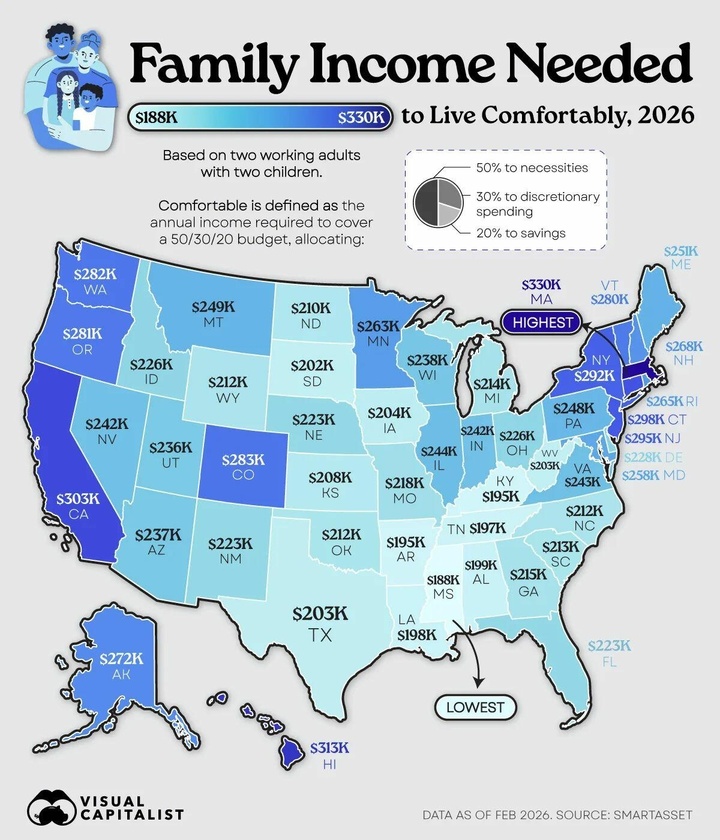
This Is The Income A Family Needs To Live Comfortably In Every US State

Here’s the short version of what it takes for a family of four to live comfortably in 2026 by state:

In Massachusetts, you’d need nearly $330,000 a year - the highest figure in the entire country. Only three states clear the $300,000 mark: Massachusetts, Hawaii, and California. At the other end of the spectrum, Mississippi is the most affordable at about $188,000. That’s a full $142,000 less than what you’d need in Massachusetts.

So… how much does a family of four need in your state?

This map shows the pre-tax income a household with two working adults and two kids needs to live comfortably in every U.S. state.

The numbers come from SmartAsset (as of February 2026). They’re based on the familiar 50/30/20 budget: 50% for necessities, 30% for discretionary spending, and 20% for savings or other goals. These aren’t bare-minimum survival numbers—they’re what it takes to live pretty well while still putting money aside.

And as Visual Capitalist notes, Massachusetts sits at the very top of that list. Massachusetts tops the ranking, with a family of four needing $329,555 per year to meet the 50/30/20 benchmark.

Hawaii follows at $313,165, while California ranks third at $302,682.

Rank State Income needed for family of four (2026)

  • 1 - Massachusetts - $329,555
  • 2 - Hawaii - $313,165
  • 3 - California - $302,682
  • 4 - Connecticut - $298,189
  • 5 - New Jersey - $295,110
  • 6 - New York - $291,533
  • 7 - Colorado - $283,213
  • 8 - Washington - $281,798
  • 9 - Oregon - $280,966
  • 10 - Vermont - $280,384
  • 11 - Alaska - $272,064
  • 12 - New Hampshire - $267,904
  • 13 - Rhode Island - $264,659
  • 14 - Minnesota - $263,078
  • 15 - Maryland - $257,837
  • 16 - Maine - $250,931
  • 17 - Montana - $249,434
  • 18 - Pennsylvania - $247,936
  • 19 - Illinois - $244,109
  • 20 - Virginia - $242,944
  • 21 - Nevada - $242,278
  • 22 - Indiana - $241,696
  • 23 - Wisconsin - $238,451
  • 24 - Arizona - $236,870
  • 25 - Utah - $235,789
  • 26 - Delaware - $228,134
  • 27 - Ohio - $226,221
  • 28 - Idaho - $226,054
  • 29 - Florida - $223,392
  • 30 - New Mexico - $223,142
  • 31 - Nebraska - $223,059
  • 32 - Missouri - $217,734
  • 33 - Georgia - $214,573
  • 34 - Michigan - $214,323
  • 35 - South Carolina - $212,909
  • 36 - North Carolina - $212,410
  • 37 - Wyoming - $212,410
  • 38 - Oklahoma - $211,910
  • 39 - North Dakota - $210,496
  • 40 - Kansas - $207,917
  • 41 - Iowa - $204,422
  • 42 - Texas - $203,424
  • 43 - West Virginia - $202,592
  • 44 - South Dakota - $201,760
  • 45 - Alabama - $198,931
  • 46 - Louisiana - $197,933
  • 47 - Tennessee - $197,267
  • 48 - Arkansas - $195,437
  • 49 - Kentucky - $194,854
  • 50 - Mississippi - $187,533

Connecticut, New Jersey, and New York aren't far behind, bringing the number of states with comfortable-income thresholds above $290,000 to six.

Colorado and Vermont Make the Top 10

As expected, many of the highest income thresholds are concentrated in the Northeast and along the West Coast.

However, Colorado has the seventh-highest threshold in the country at $283,213, ranking above Washington and Oregon.

Vermont rounds out the top 10 at $280,384, despite having the second-smallest population of any U.S. state. Meanwhile, nearby states like New Hampshire, Maine, and Rhode Island all fall outside the top 10.

Just Six States Come in Below $200,000

Despite the wide range in living costs across the country, only six states have a comfortable-income threshold below $200,000 for a family of four.

Mississippi ranks lowest at $187,533, followed by Kentucky. The states of Arkansas, Tennessee, Louisiana, and Alabama also fall below the $200,000 mark.

The gap between Massachusetts and Mississippi exceeds $142,000 per year, meaning the Massachusetts benchmark is about 76% higher.

Source

🙏To support my work, Helping to keep the signal high and the noise low:

👉 Cashapp: $thedinarian

👉 Buy me a coffee: https://buymeacoffee.com/thedinarian

👉 PayPal: Scan the QR code below 📲 or Click Here: 

👇 Crypto Donations Always Welcome 👇

XRP: r9pid4yrQgs6XSFWhMZ8NkxW3gkydWNyQX
XLM: GDMJF2OCHN3NNNX4T4F6POPBTXK23GTNSNQWUMIVKESTHMQM7XDYAIZT
XDC: xdcc2C02203C4f91375889d7AfADB09E207Edf809A6

Read full Article
post photo preview
🤖Can Decentralized AI Stop Big Tech from Owning the Future of Robotics?🤖
The race to build the future of robotics is no longer just about robots. It's about who controls the intelligence behind them.
 
Over the last three years, a small group of companies has emerged as the backbone of the AI revolution. Microsoft provides cloud infrastructure. NVIDIA supplies the chips. Google, OpenAI, Anthropic, Meta, and others develop the models. Together, they control much of the compute, data, and software stack powering modern AI.
 
Now that AI is moving into the physical world, many are asking a bigger question:
 
Will these same companies end up controlling robotics too?
 
It's a valid concern.
 
The latest generation of robots relies on enormous amounts of compute, simulation, training data, and foundation models. Many robotics startups today are built on infrastructure provided by large technology companies. NVIDIA's Omniverse is becoming a key simulation environment for robot training. Microsoft Azure is powering the training of robotics foundation models. Physical AI startups increasingly depend on hyperscale cloud infrastructure to train and deploy intelligent systems. Recent partnerships across the industry show just how central Big Tech has become to robotics development.
But while Big Tech is building the highways, another movement is trying to ensure it doesn't own every destination.
 
That movement is decentralized AI.
 
Why Decentralized AI Exists
 
The idea behind decentralized AI is simple. Instead of a handful of companies owning the models, compute infrastructure, data pipelines, and intelligence networks, these resources are distributed across thousands of participants.
 
This means anyone can contribute compute, contribute models, validate outputs and can participate.
The most visible example today is the decentralized AI network known as Bittensor (@bittensor). The network has evolved into a large ecosystem of specialized AI markets called subnets, where participants compete to provide useful machine intelligence and are rewarded based on performance. Rather than relying on a single company, intelligence is generated and validated by a distributed network of miners and validators.
 
Think of it as an attempt to build an open marketplace for AI instead of a world where intelligence is rented from a few centralized providers.
 
Why This Matters for Robotics
 
Robotics has a unique problem. Unlike chatbots, robots operate in the physical world. They need to perceive environments, make decisions, move safely and they need to learn continuously.
 
The challenge is that collecting and training on real-world robotic data is incredibly expensive. That's one reason large companies have such an advantage. They can afford the compute, simulation environments, and data infrastructure needed to train robotics models at scale.
 
This is where decentralized systems become interesting.
 
Instead of one company collecting all the data and training all the models, decentralized networks could allow thousands of contributors to participate in building robotic intelligence.
 
Imagine a future where:
  • Warehouse robots contribute operational data.
  • Delivery robots contribute navigation data.
  • Factory robots contribute manipulation data.
  • Developers contribute models.
  • Validators evaluate performance.
The resulting intelligence becomes a shared network rather than a proprietary asset.
 
That vision is beginning to emerge.
 
Bittensor's Move Toward Physical AI
 
While many people associate Bittensor (@bittensor) with language models and AI services, parts of the ecosystem are increasingly exploring embodied intelligence and robotics.
 
One example is Kinitro, a subnet focused on incentivizing the training and evaluation of embodied AI systems. The goal is to create competitive environments where developers build robotic intelligence and are rewarded based on performance.
 
The broader Bittensor ecosystem has also expanded into compute marketplaces, distributed inference systems, bandwidth infrastructure, and AI coordination layers that could eventually support robotics workloads. Several subnets now focus on decentralized compute, confidential inference, data transfer, and model training, critical components for future robotic systems.
 
In other words, the pieces are starting to appear.
 
Not a decentralized robot network yet.
 
But the infrastructure that could support one.
 
Beyond Bittensor: The Rise of Physical AI Networks
 
Bittensor isn't alone.
 
Across the industry, researchers and builders are experimenting with decentralized approaches to physical AI.
 
New research published in 2026 introduced the concept of DAO-enabled decentralized physical AI, or DePAI. The idea combines robotics, decentralized infrastructure, AI models, governance systems, and human oversight into a single framework. Instead of centralized control, robots and physical infrastructure could be coordinated through transparent rules and distributed ownership models.
 
At the same time, developers are exploring decentralized operating systems for robots that allow machines to communicate directly with each other and with distributed compute resources. These architectures are designed to make robotic systems more resilient and less dependent on a single cloud provider.
 
The goal is not simply decentralization for its own sake.
 
The goal is resilience.
 
If one server fails, the system continues.
 
If one company disappears, the network survives.
 
If one participant leaves, innovation continues.
 
But Here's the Reality
 
Decentralized AI faces the same challenge every decentralized technology faces.
 
Big Tech has resources. A lot of resources.
 
Training advanced robotics models requires enormous compute budgets, sophisticated simulation environments, access to specialized hardware, and vast amounts of real-world data.
 
That's why many robotics startups still partner with major cloud providers and AI companies. It's often the fastest path to deployment.
 
And there are legitimate concerns about whether decentralized networks can maintain quality, reliability, and security at the scale required for industrial robotics. Even researchers studying decentralized AI systems have highlighted risks around concentration, incentives, governance, and network security.
 
The challenge isn't just decentralizing intelligence.
 
It's decentralizing intelligence while maintaining performance.
 
That's much harder.
 
The Most Likely Outcome
 
The future probably won't be fully centralized. And it probably won't be fully decentralized either. Instead, we're likely heading toward a hybrid model.
 
Large technology companies will continue providing chips, cloud infrastructure, simulation platforms, and foundational research.
 
At the same time, decentralized AI networks will emerge as alternative coordination layers where intelligence, data, and economic value can be shared more openly.
 
The companies building robots may use NVIDIA hardware.
 
Train on Azure.
 
Run foundation models from OpenAI.
 
But they may also participate in decentralized data networks, decentralized compute markets, and decentralized intelligence protocols.
 
The future of robotics could end up looking less like a monopoly and more like an ecosystem.
 
The Bigger Question
 
The real question isn't whether decentralized AI can eliminate Big Tech.
 
It can't.
 
At least not anytime soon.
 
The real question is whether decentralized AI can prevent a future where a handful of companies control every robot, every model, every dataset, and every decision made by the machines operating around us.
 
As robots become workers, assistants, delivery drivers, factory operators, and even economic agents, that question becomes increasingly important.
 
Because the battle for the future of robotics is no longer about hardware.
 
It's about who owns the intelligence.
 
And that battle is just getting started.


🙏To support my work, Helping to keep the signal high and the noise low:

👉 Cashapp: $thedinarian

👉 Buy me a coffee: https://buymeacoffee.com/thedinarian

👉 PayPal: Scan the QR code below 📲 or Click Here: 

👇 Crypto Donations 👇

XRP: r9pid4yrQgs6XSFWhMZ8NkxW3gkydWNyQX
XLM: GDMJF2OCHN3NNNX4T4F6POPBTXK23GTNSNQWUMIVKESTHMQM7XDYAIZT
XDC: xdcc2C02203C4f91375889d7AfADB09E207Edf809A6

Read full Article
See More
Available on mobile and TV devices
google store google store app store app store
google store google store app tv store app tv store amazon store amazon store roku store roku store
Powered by Locals