
Dinarian888
News • Business • Investing & Finance
?The Dinarian exists because the truth deserves a platform. Covering cryptocurrency, blockchain technology, global agendas, emerging science, and consciousness — because everything is connected and people deserve to know it. Knowledge is power. ?
Interested? Want to learn more about the community?
🕵️ Crypto Mixers and Privacy Coins: Can They Resist Censorship? 🕵️

US sanctions on Tornado Cash smart contracts have created new regulatory challenges for crypto mixers and privacy coins

In response to the US Treasury sanctioning crypto mixer Tornado Cash, advocacy groups such as Coin Center have come to its defense — arguing that smart contract code is not a sanctionable entity.

With this new precedent, it is unclear if privacy coins such as Monero will face similar censorship. A hard fork update on Aug. 13 reportedly made Monero transactions harder to trace — potentially closing any back doors law agencies used to track transactions.

The view that any cryptocurrency transaction is private by default is a common misconception. In fact, the opposite is true. Blockchain data is public and transactions are traceable. Crypto mixers and privacy coins were created to provide privacy for this open financial system. But both face different uphill battles. Before analyzing the likelihood of either’s success, we need to explain how they work, where they differ and the regulatory strategy game of financial censorship.

So what is a crypto mixer?
A crypto mixer, also known as a tumbler or blender, is a transaction mixing tool or service that anyone can use to obscure a crypto wallet’s source of funds. These tools were first created for bitcoin in 2013 but became a popular alternative to privacy coins once solutions like Tornado Cash made it available for a variety of cryptoassets.

There are two types of crypto mixers: custodial and non-custodial. Custodial blenders such as blender.io are central entities that take full custody of funds to mix transactions. Users pay a fee for the service and trust the entity to return their funds once the transactions are blended.

Blender.io was the first mixer to be sanctioned by US Department of the Treasury’s Office of Foreign Assets Control (OFAC). It did not receive the same attention as Tornado Cash because it fell under the pattern of previous sanctions made against persons and entities. A North Korean state-sponsored hacker collective known as the Lazarus Group reportedly used the service after a hack against Axie Infinity that resulted in a $620 million loss.

How non-custodial crypto mixers like Tornado Cash works
With Tornado Cash, users send funds to smart contract addresses that automatically mix deposits of the same amount. They then use a zero-knowledge proof contract to prove they have the right to withdraw that amount.

For example, say you want to mix 11 ETH. Tornado Cash’s smart contracts group deposits by amounts. So you could deposit 10 ETH to the 10 ETH mixer and 1 ETH to the 1 ETH mixer. Once funds are sent to each blender, the contracts then use zero-knowledge proofs to verify you sent a deposit to each one without knowing which one was originally yours. This essentially gives you the equivalent of a withdrawal permission slip for each mixer.

So if you were to use the permission slips to withdraw both deposits, it would be close to impossible for any outside observer to identify the correct source of funds. They would see a myriad of potential options.

The tool provides pretty good financial privacy by breaking the link between the sender and receiver. But it’s not perfect; theoretically, third party blockchain intelligence could use outside data and behavior models in an attempt to deduce which transaction history belongs to the tokens on your new wallet address.

Legal challenges
On Aug. 8, 2022, OFAC added a list of addresses associated with Tornado Cash to the same list of sanctioned addresses where Blender.io ended up. This was in response to news that the Lazarus Group used the tool to launder $455 million in stolen funds.

OFAC used the same messaging and reasoning as it did Blender.io, but it did not acknowledge the key custodial difference between the two. In Coin Center’s full analysis, they argue that Tornado Cash has two separate elements: The decentralized group of governing members they call “Tornado Cash Entity” and the immutable smart contract coin mixers they call “Tornado Cash Application.”

The Tornado Cash Entity cannot update or change the Tornado Cash Application because the original creators destroyed their admin keys. The smart contracts will exist as long as the Ethereum blockchain continues to operate. So even though the Tornado Cash website is down, anyone can spin up a new front end — or interface with the smart contracts directly — that lets users access the same mixers.

The problem is that OFAC included these immutable smart contract addresses in the list of sanctions. So there are now innocent Americans with funds still in these mixers. If they attempt to move the funds, they will be breaking the law and subject to penalty. And because the application is not an entity, it has no means to petition OFAC for sanction removal.

Coin Center further argues that because the Tornado Cash Application is not an entity, OFAC did not cite the proper authority to add the smart contract addresses to the sanctions list. This marks an unprecedented move with potential constitutional issues.

In response to OFAC’s announcement, companies agreed to censor anyone connected to these addresses. The decentralized finance app Aave blocked any users that had Tornado Cash funds sent to them in a dust attack. And Circle followed by freezing 75,000 usd coin stablecoins belonging to Tornado Cash users. The Blockworks’ Empire podcast explains how that is possible in a Twitter thread.

What are privacy coins and how do they differ?
Privacy coins are cryptocurrencies that use a variety of approaches to obscure IP addresses, wallet balances and the flow of funds from public view. They differ from crypto mixers in that they make financial privacy less of a feature and more of a product. As a result, they only provide privacy to transactions made in a specific currency.

The two most popular privacy coins are Z-cash and Monero. Z-cash is a cryptocurrency that relies primarily on zero-knowledge proofs to shield transaction info. In October 2018, Z-cash announced that they fixed an 8-month-old bug in proofs that could have permitted an infinite inflation of supply. Due to transaction privacy, it was unclear how much was actually inflated.

Since this early stumble, z-cash has never returned to the highs of the 2017 bull cycle and currently ranks second to Monero in total privacy coin market cap. While monero was able to once again reach similar prices of the 2017 market, it failed to break its all-time high in 2021.

Monero is a privacy coin that offers financial anonymity through layers of privacy-enhanced blockchain encryption. Every transaction utilizes single-use stealth addresses to prevent the visibility of public address balances. So only users with a wallet’s private key can map its balance back to a public address. It also uses ring signatures to obscure the source of funds in a transaction by including random addresses in the verification signature.

Privacy challenges
The Monero protocol was upgraded on Aug. 13. While the previous version of Monero offered a layer of privacy, its complete untraceability was debatable. In 2018, critics claimed that inputs in a signature ring could be deduced through a process of elimination. And in 2021, CipherTracer reportedly patented a method that the Department of Homeland Security (DHS) uses to trace transactions.

Even if CipherTracer discovered real vulnerabilities, the extent of their impact is unclear. They didn’t disclose their methods or success rate. This previous version still provided a degree of financial privacy in the sense that it blocked anyone not willing to pay CipherTracer.

But this disincentive is less resistant to state sanctions and censorship. Theoretically, the state is more willing to spend resources in an attempt to trace addresses — especially if they suspect a connection to crime, or in some countries, political opposition.

In Canada, an effort was made to trace financial contributions to the trucker freedom convoy. The government ended up sanctioning 34 crypto wallets in connection to the movement, and Monero addresses were included in that list.

The Monero developers hope this update will close any potential vulnerability by increasing the number of transactions in a ring signature. But in response to the update, CipherTracer stated, “While Monero’s upcoming chain improvements are significant, the fundamentals of our approach to tracing probable source of funds will still apply after the fork.”

If the upgrade does succeed in closing these back doors, there is concern that OFAC may take similar actions against Monero. In an interview with CoinDesk, a Monero contributor said that, “at the moment, I’m not concerned about immediate legal action.”

“There is no direct financial incentive…for developers, unlike [the situation with] the Tornado Cash developer,” he said.

These comments seem to infer that the potential ability for the developer to profit from the use of these smart contracts makes him liable. Dutch financial crimes agency FIOD arrested a Tornado Cash developer on suspicion of laundering money through the tool. But it is unclear if that arrest was for his specific attempts to launder money or for his connection to others using it for that purpose.

Adoption challenges
Even though top privacy coins such as monero and z-cash are actively working to increase the privacy of transactions, they have not seen the same degree of adoption as leading layer-1 blockchains such as Ethereum. Many competitors, including Secret Network and Oasis Network, argue that the reason for this lag is that privacy coins do not offer a base layer of privacy that can be used to build Web3.

In 2020 Secret Network was the first privacy based blockchain to enable smart contract programmability. It lives in the Cosmos ecosystem and is working toward a vision of Web3 privacy. It has launched multiple apps such as the decentralized messaging service Altermail, and decentralized exchange SiennaSwap.

But Secret Network and its competitors face the classic challenge of an overcrowded sector. They still have a long way in overcoming the market dominance of Monero and Z-Cash. The threat of sanctions have motivated many in the Z-Cash community to explore creating their own smart contract programmability.

The future of digital financial privacy
The battle against financial privacy feels like a game of whack-a-mole. So far, the state has tried two different tools. With crypto mixers, they used the regulatory sanctions hammer. And for privacy coins, they tried blockchain intelligence sleuths.

Their approach may be, if one financial privacy method is too popular with criminals or too hard to trace, they will just shut it down with the hammer.

Advocacy groups such as Coin Center may respond by challenging such actions in court, but that process will take years. The sanctions are very likely hurting innocent Americans in the meantime.

For other privacy solutions, they may use investigations to continue in their cat and mouse chase with developer upgrades.

User adoption, though, is a key element to this game. As more people are drawn to either mixers or privacy coins, the chance of tracing transactions becomes exponentially difficult. Switching analogies, it’s like the classic police chase down a narrow alley. If the suspect reaches a bustling parade, they can dust off and subtly slip away into the crowd.

If a privacy coin, mixer or base-layer privacy solution gains mainstream adoption, it could have greater resistance to censorship. State officials would struggle to find the political backing for sweeping sanctions or technology needed to crack privacy measures. And the potential Tornado Cash sanctions fallout for Ethereum validators may pull millions more into this conversation.

https://blockworks.co/crypto-mixers-and-privacy-coins-can-they-resist-censorship/

Interested? Want to learn more about the community?
What else you may like…
Videos
Podcasts
Posts
Articles
🐝 Computer Vision Meets Real-World Hive Health Analytics! 📊

🐝 Computer Vision Meets Real-World Hive Health Analytics! 📊

​Monitoring hive entrance activity using computer vision and lightweight AI labelers is a brilliant real-world application of edge analytics! 🧠

​Why This Test Matters:

​Non-Invasive Monitoring: Tracking steady vs. frantic flight activity without disturbing the brood box gives beekeepers real-time early warnings for hive stress, swarming, or robbing. 📦

Rapid Iteration: Filtering out visual noise (like misidentifying a screw!) in early runs proves how quickly targeted single-class detection models can be tuned for precision. 🎯

🔍​Grassroots Computer Vision: Leveraging building blocks like @webuildscore demonstrates how accessible custom AI monitoring tools are becoming for everyday operational problems. 🛠️

✨​Building practical, low-latency vision systems that solve real problems is where true AI utility shines. Continuous improvement at its finest! 🚀👏

​#Score #SN44 #Bittensor #Tao #MachineLearning

00:00:40
Problem Reaction Solution 🤔

A superintelligence would have stopped this before it even started.

Wait, thats their point... Problem Reaction Solution. In the future, expect Superintelligence Police Online.

I can’t stop thinking about this… before hackers stole $6.4 billion from Binance, they spent days rehearsing the attack in public. The test transactions on Ethereum were worth only a few dollars. Nobody stopped them.

Bloomberg reconstructed what happened. Once the code worked, the hackers launched the real attack across multiple blockchains.

Then I reached the detail that doesn’t feel real. Some of the compromised wallets kept receiving fresh funds from Binance while the hackers were draining them. The attackers emptied a wallet, Binance refilled it, and they emptied it again. For a period of time, the exchange was effectively feeding new money into its own robbery.

Binance co-founder Yi He was at home in Abu Dhabi. She reportedly discovered the breach while scrolling X before bed. Imagine opening Twitter and learning...

00:00:16
🤫 WE CAN'T TALK ABOUT IT 🤫

🌧️ From rain-soaked diners ☕ to ancient coin forging in 589 BC 🪙, secret Non-Disclosure Agreements surround the financial world 💼.

💥 Suits marching with NDA signs 📄, high-octane skydiving onto private jets 🛩️, and BlackRock’s Larry Fink refusing to answer about an XRP ETF 🤐.

Is $XRP the hidden bridge for global finance? 🌐
⚡ Read between the lines! 📜

⚠️ Not Financial Advice ⚠️

🎥 Created by @BUNGAMEDINGOS

#XRP #Crypto #Bitcoin #BlackRock #XRPLedger #CryptoNews

00:07:06
🚨 Chutes is being framed as a Hyperliquid-style breakout for decentralized AI inference, with live revenue, verified GPU infrastructure, and a direct challenge to centralized cloud AI 🚨

Chutes is gaining attention as a decentralized AI inference platform that claims to combine real usage, cryptographic verification, confidential computing, and open-source infrastructure into a working production system. The thesis is simple: instead of trusting Big Tech clouds with AI workloads, users get a distributed compute layer built around verification and privacy.

🔑 Key points

🔹 Chutes is live in production and reportedly scaled to more than 1,170 active GPU nodes, including large numbers of Nvidia H200s and Blackwell-class hardware.

🔹 The platform says it has processed nearly 38 trillion tokens since launch across 53 deployed applications and more than 700,000 registered users.

🔹 The team reportedly cut unprofitable usage programs, reduced total token volume, and still improved revenue efficiency, with revenue per GPU rising sharply after removing subsidized traffic.

🔹 Chutes is using post-quantum cryptography, trusted execution environments, and Nvidia confidential ...

🚨 Chutes is being framed as a Hyperliquid-style breakout for decentralized AI inference, with live revenue, verified GPU infrastructure, and a direct challenge to centralized cloud AI 🚨
🚨 JPMorgan’s criticism of the CLARITY Act is fueling a fresh power struggle over who gets to write America’s crypto rules 🚨

A new clash is emerging between legacy finance and crypto legislation after JPMorgan CEO Jamie Dimon reportedly warned that the CLARITY Act could let crypto firms offer bank-like products without bank-level oversight. The dispute is quickly turning into a larger fight over regulation, competitiveness, and who controls the future architecture of digital finance in the United States.

🔑 Key points

🔹 Jamie Dimon reportedly called the CLARITY Act a threat to the financial system, arguing it could allow crypto firms to offer yield-like products while avoiding the capital, reserve, and oversight burdens traditional banks face.

🔹 Senator Cynthia Lummis pushed back publicly, framing the issue as a global strategic race and warning that if the U.S. does not set digital asset standards, other powers will.

🔹 The core tension is whether the bill creates legitimate regulatory clarity or simply opens the door to regulatory arbitrage for crypto platforms operating outside the traditional banking...

🚨 JPMorgan’s criticism of the CLARITY Act is fueling a fresh power struggle over who gets to write America’s crypto rules 🚨
👉 Coinbase just launched an AI agent for Crypto Trading

Custom AI assistants that print money in your sleep? 🔜

The future of Crypto x AI is about to go crazy.

👉 Here’s what you need to know:

💠 'Based Agent' enables creation of custom AI agents
💠 Users set up personalized agents in < 3 minutes
💠 Equipped w/ crypto wallet and on-chain functions
💠 Capable of completing trades, swaps, and staking
💠 Integrates with Coinbase’s SDK, OpenAI, & Replit

👉 What this means for the future of Crypto:

1. Open Access: Democratized access to advanced trading
2. Automated Txns: Complex trades + streamlined on-chain activity
3. AI Dominance: Est ~80% of crypto 👉txns done by AI agents by 2025

🚨 I personally wouldn't bet against Brian Armstrong and Jesse Pollak.

👉 Coinbase just launched an AI agent for Crypto Trading

🖼️ Hippius launches WordPress media offloader

The Hippius Media Offloader plugin lets WordPress site owners move existing media files to Hippius storage and automatically offload new uploads. It connects through an S3-compatible API and can replace media URLs with Hippius-hosted versions.

🔑 Key points

🔹 Existing media migrates in bulk: Site owners can move their current media library in batches and monitor progress, errors, and storage use.

🔹 New uploads can offload automatically: Once enabled, new WordPress media uploads are transferred to Hippius in the background.

🔹 Local backups are optional: Users can keep local copies during migration or delete them after successful transfer to save server space.

🔹 Storage uses distributed shards: Hippius says Arion splits files into 30 shards—10 data and 20 parity—across network nodes.

🔹 S3 setup is required: Users need a Hippius account, funded balance, S3 credentials, and a bucket they create manually. Storage can be paid for by card, TAO, ...

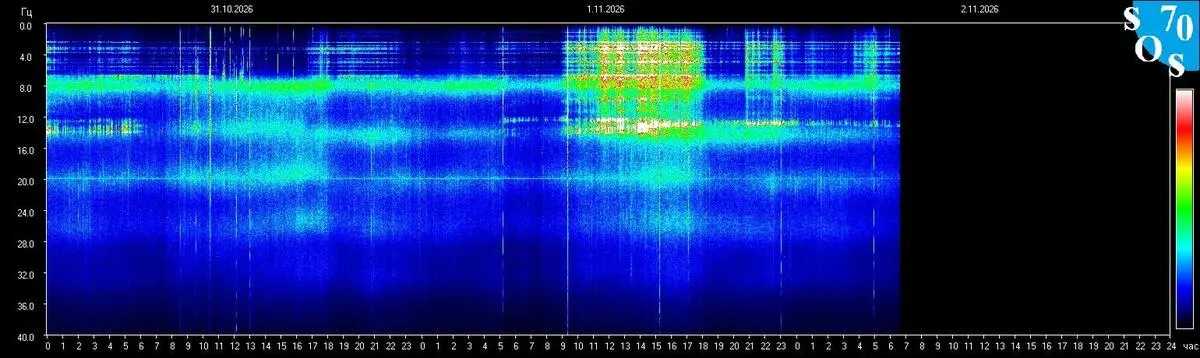
🌎Schumann Resonance Today 11/3🌎

Right now the Schumann resonance fundamental sits at 7.83 Hz, with geomagnetic activity quiet (Kp 1.7).

Solar Flicker, Low Kp, Firm Baseline Today: A B8.0 flare and gentle solar wind at 383 km/s leave the magnetosphere largely undisturbed. Kp sits at 2.67, keeping the electromagnetic backdrop stable.

post photo preview

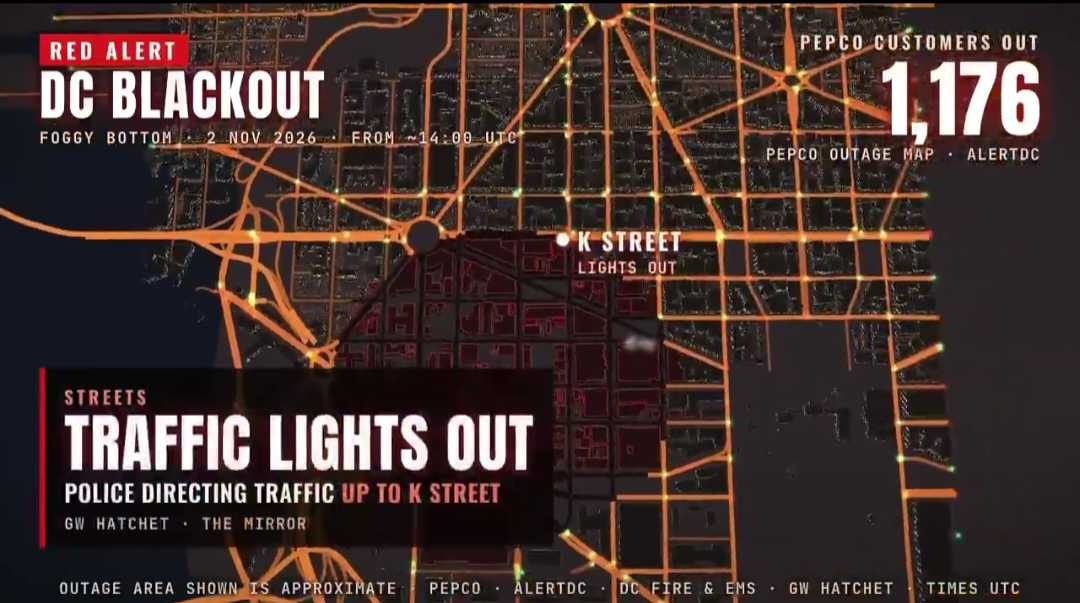
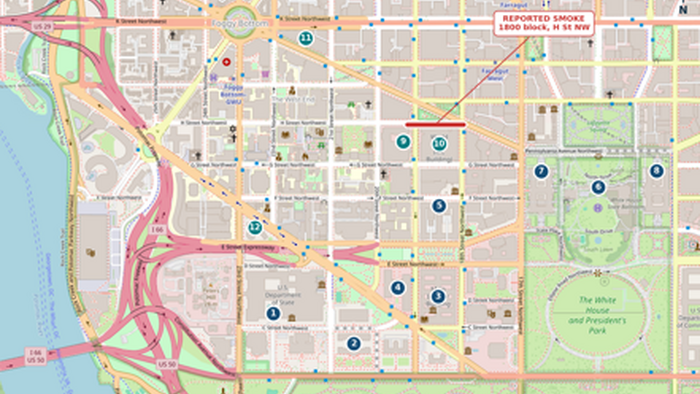
⚡ Foggy Bottom power outage affects State Department facilities

A substation incident in Washington, D.C.’s Foggy Bottom neighborhood left more than 1,100 Pepco customers without power on November 2, including several State Department facilities. Pepco said the cause was under investigation and had not provided an estimated restoration time when the article was published.

🔑 Key points

🔹 Outage affected 1,100 customers: Pepco reported power loss around its I Street Substation.

🔹 State Department sites were affected: The department confirmed that multiple facilities experienced an unscheduled power loss.

🔹 Traffic lights also lost power: The outage affected stoplights in the area, according to local reports.

🔹 Cause remains under investigation: Pepco described an “event” at the substation but did not say what caused it.

🔹 No restoration estimate was available: Crews were assessing the situation and working to restore service safely.

🔹 Suspicion is not evidence: The article calls ...

post photo preview
post photo preview
🎯What’s In Your Vault? — 2026 Edition🎯

Sixteen years ago, I posed a question that appeared to be about money but was never really about money at all. What's In Your Wallet? was written at a moment when the world remained intoxicated by the illusion that a representation of value and value itself were interchangeable. The distinction seemed trivial because the machinery of modern finance operated smoothly enough to conceal it. A bank balance purchased goods. A brokerage statement could be exchanged for assets. A warehouse receipt represented commodities. A title represented property. A promise represented delivery. The system functioned, and because it functioned, few bothered to examine the assumptions upon which it rested.

Yet beneath the smooth functioning of the machine lurked a subtle substitution. Somewhere along the way we ceased valuing the thing and began valuing the description of the thing. We stopped demanding possession and settled for evidence of possession. We became comfortable owning records instead of realities, claims instead of assets, promises instead of substance. The map became more important than the territory because most people never wandered far enough from the roads to discover that the two were not the same.

Reading those observations in 2026 feels less like revisiting an old essay and more like observing a fault line that has slowly widened beneath the surface of the global financial order. What has changed is not the distinction itself. What has changed is that the institutions most responsible for maintaining the abstraction appear increasingly unwilling to trust it.

Around the world, central banks have begun bringing gold home. Not merely purchasing gold, though that is certainly occurring, but repatriating it. Bullion that once rested comfortably in the vaults of London and New York is being moved into domestic custody. Public explanations invoke geopolitical uncertainty, sanctions exposure, strategic resilience, and sovereign security. None of those explanations are incorrect. They are simply incomplete. They describe the circumstances without illuminating the realization that appears to be driving the behavior.

A gold bar in your vault is not the same thing as a claim upon a gold bar in someone else's vault. Since the Templars in Jerusalem communicating with the courts of Europe, promises are not the thing that's promised. They never were.

For decades that distinction could be ignored because confidence in the system remained sufficiently high that possession appeared unnecessary. The custodians were trusted. The networks functioned. The legal frameworks appeared durable. The infrastructure seemed permanent. Under those conditions, claims and assets could masquerade as equivalents because the distance between them was rarely tested. Yet every system eventually encounters moments when assumptions become visible. The freezing of sovereign reserves reveals that ownership and access are not identical. Financial crises reveal that liquidity and solvency are not identical. Infrastructure failures reveal that existence and availability are not identical. Again and again reality intrudes upon abstraction and reminds us that the world beneath the ledger still matters.

This is why the movement of gold deserves more attention than the declarations of economists, politicians, central bankers, or global forums. The repatriation of gold is not fundamentally a commodity story, an inflation story, or even a monetary story. It is a custody story. It is a sovereignty story. It is an acknowledgment that possession remains the final court of appeal whenever confidence begins to wobble.

The irony is difficult to miss. At precisely the moment civilization celebrates digital currencies, tokenized assets, algorithmic settlement systems, cloud-based records, and increasingly abstract forms of ownership, many of the institutions responsible for preserving national wealth appear to be moving in the opposite direction. Public narratives race toward virtuality while institutional behavior quietly migrates toward physical custody. The speeches point toward digitization while the bullion trucks point toward reality.

Perhaps nowhere does this contradiction become more visible than when contemplating the fragility of the infrastructure upon which modern finance rests. We speak confidently of balances, portfolios, reserves, pensions, derivatives, and increasingly digital assets as though they possess an existence independent of the systems that record them. Yet the entire architecture rests upon a remarkably delicate foundation of electricity, communications, computation, synchronization, and trust. We have become so accustomed to continuity that we mistake continuity for permanence.

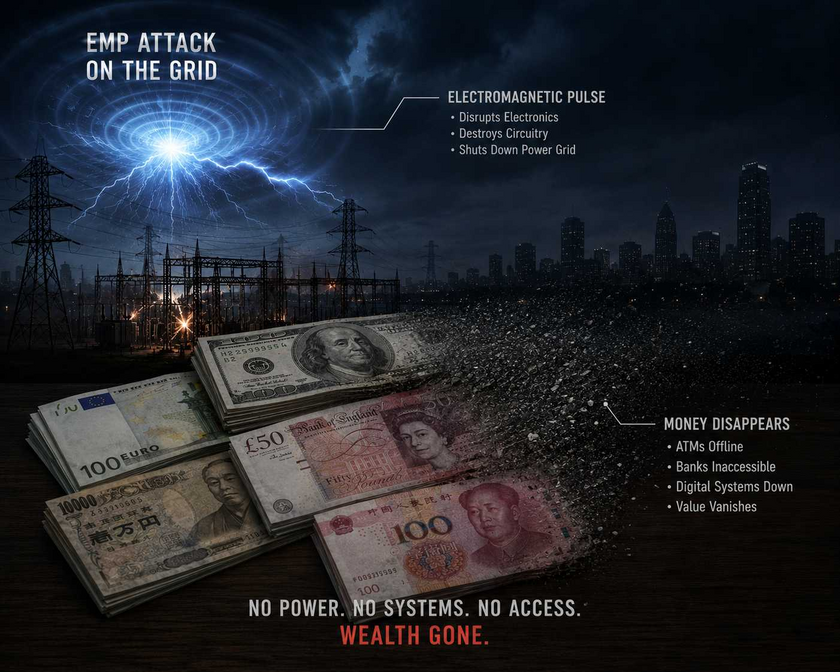
Consider not catastrophe but interruption. Consider a Carrington-scale solar event, a successful cyberattack, a cascading grid failure, or an electromagnetic pulse. The specific mechanism matters less than the principle. The lights go out. The servers stop responding. The networks cease synchronizing. The endless choreography of verification pauses. Legal claims may survive. Contracts may survive. Accounting entries may survive. Yet the practical ability to verify, transfer, access, or exercise those claims becomes uncertain. The abstractions remain theoretically intact while becoming functionally irrelevant.

Gold occupies a peculiar place within this thought experiment because it exists outside the thought experiment. It requires no password, no network connection, no authentication server, no intermediary, and no continuous electrical infrastructure to affirm its existence. The ledger may disappear. The gold remains. Whether one views gold as a monetary asset, a strategic reserve, or simply a historical curiosity, its persistence reveals something deeper about the nature of value itself. Assets that derive their existence from the systems that record them are fundamentally different from assets that exist independently of those systems.

What fascinates me, however, is not the rhetoric surrounding the so-called Great Reset, because the phrase itself has become one of the most effective distractions of the modern era. During the COVID years, populations were conditioned into increasingly reflexive forms of polarization in which every issue was immediately translated into opposing camps, every observation became a declaration of allegiance, and every question became a test of ideological loyalty. One side treated the Great Reset as evidence of a coordinated conspiracy while the other dismissed it as evidence of irrational paranoia. Both reactions produced the same outcome. Attention became fixed upon the slogan while remaining safely distant from the structure beneath it.

History has never required a committee to produce a reset. Resets emerge whenever claims become sufficiently detached from assets, whenever promises become sufficiently detached from productive capacity, whenever leverage becomes sufficiently detached from resilience, and whenever abstractions become sufficiently detached from reality. Long before a reset acquires a name, it exists as a tension embedded within the architecture itself.

This is why the most revealing actions in history are rarely the ones announced from podiums. They are the quiet movements that occur beneath the rhetoric. While populations argue over narratives, central banks move bullion. While commentators debate ideology, nations secure custody. While attention remains fixed upon political theater, the custodians of monetary power appear to be asking an older and more fundamental question concerning what survives when confidence falters, when access becomes uncertain, and when the systems responsible for recording ownership can no longer be assumed to function exactly as they did yesterday.

History repeatedly demonstrates that major transitions rarely emerge from the causes later assigned to them. Wars, sovereign defaults, financial crises, technological disruptions, infrastructure failures, and natural disasters frequently function as explanatory narratives that make visible contradictions that had already been accumulating for decades. The triggering event receives the blame because it is easier to understand than the architecture that rendered the event consequential. Yet the architecture is always where the real story resides. The event merely exposes what was already true.

Seen from this perspective, the most important question is not whether a particular organization intends to implement a Great Reset. The more important question concerns the conditions under which resets become inevitable. Whenever claims multiply faster than assets, whenever obligations expand faster than productive capacity, whenever financial abstractions drift sufficiently far from physical realities, tensions accumulate that eventually demand reconciliation. That reconciliation may arrive through inflation, restructuring, default, crisis, technological disruption, or events conveniently attributed to forces beyond human control, but the mechanism remains secondary to the principle. Reality eventually reasserts itself because reality is the only foundation upon which any abstraction can ultimately stand.

Viewed through that lens, the repatriation of gold appears less like a financial decision than an institutional acknowledgment that the distinction between claims and assets still matters. It represents a quiet recognition that resilience and possession acquire increasing importance precisely when complexity and uncertainty begin to rise. It suggests that beneath the public narratives, beneath the political theater, and beneath the endless distractions that dominate contemporary discourse, some of the world's most consequential actors may be asking the same question that inspired an essay sixteen years ago. What do you actually possess when the systems recording possession become uncertain?

The question is not fundamentally about gold. It is not fundamentally about vaults. It is not fundamentally about central banks. It is a question about the difference between a thing and a description of a thing, between ownership and access, between claims and assets, between abstractions and realities. It is the question that emerges whenever a civilization becomes sufficiently dependent upon representations that it forgets to examine the realities those representations are intended to describe.

Sixteen years ago I asked what was in your wallet. Watching nations quietly move bullion across oceans and into sovereign custody, the question feels sharper today than it did then. Not because the answer has changed, but because the institutions themselves appear increasingly unwilling to pretend that a claim and an asset are the same thing. The distinction sounded eccentric in 2010. It sounds increasingly obvious in 2026. The most interesting question is whether the rest of us will recognize the significance of that realization before history once again forces the issue on its own terms.

Source

🙏To support my work, Helping to keep the signal high and the noise low:

👉 Cashapp: $thedinarian

👉 Buy me a coffee: https://buymeacoffee.com/thedinarian

👉 PayPal: Scan the QR code below 📲 or Click Here: 
👇 Crypto Donations 👇

XRP: r9pid4yrQgs6XSFWhMZ8NkxW3gkydWNyQX
XLM: GDMJF2OCHN3NNNX4T4F6POPBTXK23GTNSNQWUMIVKESTHMQM7XDYAIZT
XDC: xdcc2C02203C4f91375889d7AfADB09E207Edf809A6

Read full Article
post photo preview
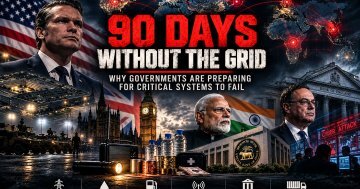
⚠️90 DAYS WITHOUT THE GRID⚠️
Why Governments Are Preparing for Critical Systems to Fail

MIND BEND THEORY | DOCUMENTED INVESTIGATION

The United States is preparing major military installations to continue operating if civilian infrastructure goes down. Britain is telling households to prepare for days without essential services. India is warning that an attack on the financial system can weaken a nation. And the Bank of England is asking what happens when cyber defenses fail—not if they can prevent every attack.

Individually, each development has an explanation.

Put them beside one another, however, and a larger pattern becomes visible.

Over the span of only a few weeks, governments and financial authorities in the United States, United Kingdom and India have publicly discussed preparations for disruptions involving some of the systems modern society depends upon most:

Power.

Water.

Fuel.

Communications.

Banking.

Supply chains.

This does not establish that these governments are preparing for one secret event.

There is no public evidence of a coordinated countdown, predetermined blackout date or single intelligence warning connecting them.

But there is something here that can be documented.

Governments are increasingly planning around a question that sounds very different from traditional emergency preparedness:

What happens when the systems we normally assume will be available are no longer available?

And in the United States, that question has now reached the Pentagon.

DOCUMENT 01

UNITED STATES — FORTRESS AMERICA

On September 30, 2026, Defense Secretary Pete Hegseth established a program called FORTRESS America.

The acronym stands for:

Federal Operations for Resilience, Troop Resources, Energy, Supply and Survivability.

The program addresses a vulnerability that rarely receives much public attention:

The world's most powerful military still depends extensively on civilian infrastructure.

Electric grids.

Commercial supply chains.

Communications infrastructure.

Fuel.

Foreign sources of critical materials.

FORTRESS America is intended to reduce those dependencies.

The Pentagon's own public description says the initiative is designed to ensure that major U.S. military installations generate independent power so that bases remain operational even if the civilian grid is taken down by cyberattack or sabotage.

It goes beyond electricity.

The program includes five major areas:

Energy independence

Installation hardening and cyber resilience

Supply-chain and defense-industrial-base resilience

Strategic defense reserves

Space and spectrum resilience

The Pentagon also wants deeper reserves of critical supplies so military operations can continue when ordinary supply lines are disrupted.

The underlying idea is simple:

The military should be capable of functioning even when the infrastructure surrounding it cannot.

An October 7 implementation memorandum obtained by DefenseScoop shows that the Pentagon had already begun establishing the FORTRESS America Program Office and assigning officials to implement those objectives.

Then another piece of the story emerged.

DOCUMENT 02

THE 90-DAY REQUIREMENT

On October 25, Fox News published details from additional FORTRESS America documents its reporters reviewed.

According to that reporting, major continental U.S. military installations are being prepared to sustain essential operations for at least 90 days without outside support.

The essential systems reportedly include:

Power.

Water.

Fuel.

Communications.

Think about the distinction carefully.

The Pentagon isn't telling Americans that the United States will lose electricity for 90 days.

It isn't predicting a 90-day blackout.

Military contingency planning deliberately prepares for scenarios officials hope never occur.

But preparing installations for this possibility tells us something about the scenario being considered.

The Pentagon is building resilience around the possibility that a sufficiently serious conflict or attack could interfere with the civilian systems on which military installations normally depend.

The publicly released FORTRESS material specifically discusses:

Cyberattack.

Sabotage.

Grid disruption.

Foreign supply-chain disruption.

Attacks against installations.

And prolonged military contingencies.

That makes the 90-day requirement significant—but it must be described accurately.

Mind Bend Theory verification note:

The September 30 FORTRESS America program itself is documented publicly.

The October 7 implementation memorandum has been reported and described by DefenseScoop.

The 90-day requirement, however, currently comes from documents reviewed by Fox News, rather than a primary 90-day document independently published for the public.

That distinction matters.

We follow the documents as far as they take us—and no farther.

DOCUMENT 03

UNITED KINGDOM — BE READY FOR THREE DAYS

Now cross the Atlantic.

On October 22, the British government launched its new Be Ready campaign.

This time the audience wasn't the military.

It was ordinary households.

The UK government is asking households that are able to do so to prepare to remain self-sufficient for approximately three days during an emergency.

The government specifically discusses disruptions affecting:

Power.

Water.

Phones.

Internet access.

A Parliamentary Written Statement issued the same day explicitly states:

“The updated advice calls on households to be self-sufficient for three days in the case of an emergency.”

The government recommends maintaining three days of bottled water and non-perishable food.

Its expanded preparedness guidance includes:

Approximately three litres of drinking water per person per day

Three days of non-perishable food

Battery-powered or wind-up radio

Torch and spare batteries

Charged power bank

Essential medications

First-aid supplies

Blankets and warm clothing

Important telephone numbers written down

Basic hygiene supplies

Cash

Why cash?

Because during some disruptions, electronic payment systems and ATMs may not function normally.

That creates an important connection between infrastructure and finance.

Electricity isn't isolated from banking.

Communications aren't isolated from payments.

Modern infrastructure is interconnected.

And failure can move through those connections.

DOCUMENT 04

INDIA — “WARS ARE NOT FOUGHT WITH WEAPONS ALONE”

Three days later, on October 25, another statement appeared.

This one came from Indian Prime Minister Narendra Modi.

Modi was inaugurating the Reserve Bank of India's newly established Data Centre and Cybersecurity Training Institute in Bhubaneswar.

The facilities are designed to strengthen the technological foundations and cybersecurity resilience of India's financial system.

Four data centres will host mission-critical payment and settlement systems.

But Modi's explanation of why this matters went beyond ordinary cybersecurity.

His official statement says:

“Nowadays, wars are not fought with weapons alone; a nation can also be weakened by attacking its economy.”

He continued by saying India's growing economy requires its banking system to be protected against cyber looters and cyber terrorists.

That puts another critical system into the picture:

Money.

A modern economy depends on digital banking infrastructure almost as heavily as it depends on electricity and telecommunications.

Payment systems move commerce.

Banks hold liquidity.

Settlement systems move money between financial institutions.

Data centres keep those networks functioning.

Disrupt the financial infrastructure badly enough and the consequences don't remain inside banks.

They reach businesses.

Supply chains.

Payroll.

Purchasing.

Markets.

And households.

DOCUMENT 05

BANK OF ENGLAND — WHAT IF CYBER DEFENSE FAILS?

There is another document worth reading.

On June 30, Bank of England Deputy Governor Sarah Breeden delivered a speech titled:

“Agents of Change.”

The subject was artificial intelligence and financial stability.

One section deserves particular attention.

Breeden warned that advanced AI systems are becoming increasingly capable of identifying and chaining together cyber vulnerabilities.

That changes the nature of cyber risk.

AI can help defenders.

But the same capabilities can potentially increase the speed and effectiveness of attackers.

The important change in thinking comes afterward.

Preventing attacks is no longer enough.

Financial institutions must also prepare to recover after a successful attack.

Breeden raised the possibility of simultaneous disruption across multiple financial firms.

She then asked whether critical financial institutions may eventually require completely separate failover capabilities—or even the ability to rebuild compromised core systems from “bare metal.”

In October, Reuters reported that the Bank of England was pushing financial institutions further toward this type of recovery planning.

That represents a subtle but significant change in the question.

It isn't simply:

How do we stop the attack?

It's becoming:

What happens if we don't?

And:

How do we keep the system functioning afterward?

CONNECT THE DOCUMENTS

Now put the documents beside one another.

UNITED STATES

Military installations are being hardened so essential operations can continue when civilian infrastructure is disrupted.

UNITED KINGDOM

Households are being told to prepare for three days without services they normally assume will remain available.

INDIA

The prime minister publicly warns that modern conflict can weaken a country by attacking its economy and calls for stronger protection of banking infrastructure.

BANK OF ENGLAND

Financial authorities are examining recovery scenarios in which cyber defenses have already failed and multiple institutions could potentially be disrupted simultaneously.

These aren't identical programs.

They aren't even aimed at the same people.

And there is currently no public evidence demonstrating that they were coordinated.

But they share one important assumption:

CRITICAL SYSTEMS CAN FAIL.

And resilience therefore cannot begin after the failure occurs.

It has to exist beforehand.

THE SYSTEM BEHIND THE SYSTEM

This is where the story becomes bigger than individual announcements.

Modern infrastructure isn't a collection of isolated systems.

It's a network.

Consider what happens when electricity fails.

Without power, telecommunications eventually become difficult to maintain.

Without communications, electronic payments can be affected.

Fuel pumps require electricity.

Water systems depend on pumping and treatment infrastructure.

Businesses depend on payment processing.

Supply chains depend on communications, transportation and fuel.

Hospitals require electricity, communications, water, medicine and logistics simultaneously.

A serious disruption doesn't necessarily remain inside the system where it started.

It can propagate.

POWER → COMMUNICATIONS → BANKING → COMMERCE → SUPPLY CHAINS

And the dependency runs in multiple directions.

That interconnectedness is precisely why governments plan for resilience.

WHAT THIS DOES NOT PROVE

Mind Bend Theory exists to examine unusual patterns.

But a pattern isn't automatically proof of a conspiracy.

There is currently no public evidence showing that Washington, London and New Delhi are secretly preparing for the same scheduled event.

There is no verified date for a coming global blackout.

There is no public document establishing an imminent 90-day collapse of the American electrical grid.

And the Pentagon's 90-day military resilience requirement should not be interpreted as a prediction that Americans will lose electricity for 90 days.

That would go beyond the evidence.

What the evidence actually establishes is interesting enough.

Governments increasingly consider disruption of power, communications, supply chains and financial infrastructure plausible enough to justify concrete preparation.

The UK is preparing households.

The United States is hardening military infrastructure.

India is strengthening the technological backbone of its financial system.

The Bank of England is thinking about how banks recover after cyber defenses fail.

That isn't speculation.

It's in the documents.

THE QUESTION

Perhaps the most important change isn't what governments believe will happen.

It's what they're preparing to survive.

For decades, infrastructure security focused heavily on preventing failure.

The emerging model looks different:

Assume something eventually gets through.

Assume something eventually goes down.

Build the ability to continue operating anyway.

The Pentagon calls that resilience.

The UK calls it being ready.

Central banks call it operational resilience.

Different terminology.

Same fundamental question:

WHAT STILL WORKS WHEN THE SYSTEM DOESN'T?

DOCUMENT TRAIL

Read the Evidence Yourself

Mind Bend Theory strongly encourages readers to examine the original material rather than relying solely on our interpretation.

🇺🇸 DOCUMENT 01 — FORTRESS America Establishment

September 30, 2026

Defense Secretary Pete Hegseth's memorandum establishes FORTRESS America as a Department of Defense resilience program.

The publicly reported memorandum establishes the program around installation resilience, independent energy, strategic reserves, supply chains and related national-defense infrastructure.

Source type: Pentagon memorandum / official announcement.

🇺🇸 DOCUMENT 02 — FORTRESS America Implementation Memorandum

October 7, 2026

DefenseScoop obtained the memorandum from Under Secretary for Acquisition and Sustainment Michael Duffey directing officials to begin operationalizing the FORTRESS America Program Office.

It identifies five foundational pillars, including energy independence, installation hardening and cyber resilience, strategic reserves and supply-chain resilience.

Source type: Pentagon memorandum obtained by DefenseScoop.

🇺🇸 DOCUMENT 03 — 90-Day FORTRESS Requirement

October 25, 2026

Fox News reports that documents it reviewed require major continental U.S. installations to sustain essential operations for at least 90 days without outside support.

Source type: Journalistic reporting based on documents reviewed by reporters.

Important: This is not currently being presented by Mind Bend Theory as a publicly released primary 90-day Pentagon document.

🇬🇧 DOCUMENT 04 — UK Cabinet Office Be Ready Announcement

October 22, 2026

The Cabinet Office announces the three-year Be Ready campaign and describes preparation for disruption affecting power, water, phones and internet.

Source type: Official UK government publication.

🇬🇧 DOCUMENT 05 — Parliamentary Written Statement HCWS409

October 22, 2026

The UK Parliament records the government's explicit recommendation that households prepare to remain self-sufficient for three days.

Source type: Official Parliamentary record.

🇬🇧 DOCUMENT 06 — Be Ready Household Emergency Checklist

The government's practical household guidance provides recommendations for water, food, radio, lighting, medication, power banks, emergency cash and other supplies.

Source type: Official UK government preparedness guidance.

🇮🇳 DOCUMENT 07 — Prime Minister of India / RBI Cybersecurity Facilities

October 25, 2026

Official statement documenting the opening of the Reserve Bank of India's Data Centre and Cybersecurity Training Institute and Modi's warning that countries can be weakened through attacks against their economies.

Source type: Official Government of India statement.

🇬🇧 DOCUMENT 08 — “Agents of Change” — Sarah Breeden

June 30, 2026

The Bank of England deputy governor discusses rapidly advancing AI cyber capabilities, simultaneous disruption across financial institutions, separate failover infrastructure and potentially rebuilding compromised systems from bare metal.

Source type: Official Bank of England speech.

DOCUMENT 09 — Bank of England Cyber-Recovery Reporting

October 15, 2026

Reuters reports on the Bank of England's push for stronger recovery capabilities against AI-enabled cyberattacks, including bare-metal recovery.

Source type: Independent reporting.

MIND BEND THEORY

Follow the documents. Separate what they prove from what they don't.

Then ask why the preparation is happening now.

Documents attached to the investigation

FORTRESS America — Sept. 30 memorandum record
Pentagon FORTRESS America implementation memorandum — DefenseScoop
FORTRESS America 90-day documents — Fox News investigation
UK Cabinet Office — Be Ready announcement
UK Parliament — Written Statement HCWS409
India PM's Office — RBI Data Centre & Cybersecurity Training Institute
Bank of England — Sarah Breeden, “Agents of Change”
Reuters — Bank of England cyber-recovery warning

Source

🙏To support my work, Helping to keep the signal high and the noise low:

👉 Cashapp: $thedinarian

👉 Buy me a coffee: https://buymeacoffee.com/thedinarian

👉 PayPal: Scan the QR code below 📲 or Click Here: 

👇 Crypto Donations 👇

XRP: r9pid4yrQgs6XSFWhMZ8NkxW3gkydWNyQX
XLM: GDMJF2OCHN3NNNX4T4F6POPBTXK23GTNSNQWUMIVKESTHMQM7XDYAIZT
XDC: xdcc2C02203C4f91375889d7AfADB09E207Edf809A6
Read full Article
September 13, 2026
post photo preview
Revolut Leak Shows the Cost of Constant ID Collection
Revolut’s mistake is the news, but the bigger problem is the growing number of companies being encouraged or required to keep copies of our most sensitive identity documents.

Online bank Revolut has revealed that it gave out sensitive personal and financial information of an undisclosed number of its customers in response to a fake government request.

The information that was handed over to an “unauthorized third party” reportedly includes names, dates of birth, occupations, addresses, phone numbers, account numbers, transaction histories (including Bitcoin), and even copies of government-issued IDs and onboarding verification selfies.

Revolut claims that derived biometric face data was not.

The company said that the data was handed over in response to an email that came from a real government agency’s domain, but was not actually sent or authorized by that agency.

The email passed several authentication checks (SPF, DKIM, and DMARC) that are designed to establish the authenticity of a message’s origin and integrity, but do not verify the legitimacy of the legal request itself.

Revolut said that it complied with the request “under the reasonable belief that it was an authentic government agency request” – and only later found out that it was not.

Revolut said it later realized its mistake, blocked the email address, and reported the incident to the relevant authorities.

Revolut said that only a “limited” number of its customers were affected by the data leak, and that the company’s systems were not hacked, nor was any money stolen.

The story broke on September 11 when Revolut customers started receiving an email notice about a data leak, and the news was picked up by media outlets the following day.

Revolut notice explaining customer identity and financial data was shared after an unauthorized government email request.

The reason this is a recurring problem is that companies are keeping highly sensitive information about their customers’ identities, and sometimes even financial transactions, for a long time, and this data is then available to be disclosed to third parties – either in response to valid legal requests, or, as in the case of Revolut, fake ones.

One reason for this is know your customer (KYC) and anti-money laundering (AML) rules. Revolut’s current UK customer privacy notice spells it out: the company generally keeps personal data of UK customers for no more than seven years after the relationship ends, and sometimes longer – for legal reasons.

This means that even if you close your account, your identity documents don’t disappear.

And while the incident with Revolut happened in the financial sector, it’s by no means the only one that requires customers to hand over sensitive identity information. Discord, a popular chat service, said in an October 9, 2025 security update that government ID photos of approximately 70,000 users may have been exposed after a third-party customer service provider got hacked.

This was not a financial service, nor the same type of attack. But the result was similar – because the underlying business process was the same: requiring and storing sensitive identity documents. In the case of Discord, these were used to review age-related appeals.

It’s hard to do anything about a copy of your old passport, or a photo of your face, or a record of your past transactions. These can be used to identify and profile you, and can be used to carry out targeted fraud. And this can happen even if the initial disclosure didn’t result in financial loss.

The more companies are forced to collect and store such information, and the more of it they have, the more opportunities there are for this data to be leaked, either by the company itself or a third party it works with. That's what makes governments' push for more ID checks just to access ordinary parts of life so reckless.

Source

🙏To support my work, Helping to keep the signal high and the noise low:

👉 Cashapp: $thedinarian

👉 Buy me a coffee: https://buymeacoffee.com/thedinarian

👉 PayPal: Scan the QR code below 📲 or Click Here: 

👇 Crypto Donations 👇

XRP: r9pid4yrQgs6XSFWhMZ8NkxW3gkydWNyQX
XLM: GDMJF2OCHN3NNNX4T4F6POPBTXK23GTNSNQWUMIVKESTHMQM7XDYAIZT
XDC: xdcc2C02203C4f91375889d7AfADB09E207Edf809A6
Read full Article
See More
Available on mobile and TV devices
google store google store app store app store
google store google store app tv store app tv store amazon store amazon store roku store roku store
Powered by Locals